Canvas Breach: Login Portals Defaced in Extortion Attack
Instructure says a Canvas incident exposed names, emails, student IDs, and user messages at affected organizations, while login pages were later altered during the same incident.

CallPhantom Scam Apps Reached 7.3M Google Play Installs
ESET says 28 CallPhantom apps in Google Play sold fake call, SMS, and WhatsApp history reports, turning curiosity into paid subscriptions and harder-to-refund charges.
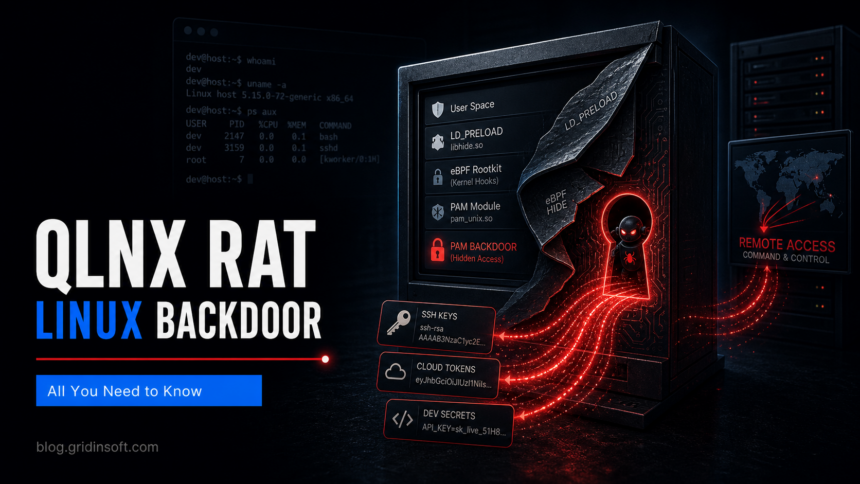
QLNX RAT Targets Linux Developer and Cloud Credentials
Trend Micro reports QLNX, a Linux-focused Quasar RAT variant that combines persistence, rootkit-style hiding, PAM backdoor access, and credential theft from developer and cloud environments.
TCLBANKER Banking Trojan Spreads Through WhatsApp and Outlook
Elastic reports that TCLBANKER hides inside a fake peripheral-device installer, uses DLL sideloading, and spreads through WhatsApp and Outlook while targeting Brazilian banking users.
PyPI ZiChatBot Packages Linked to Suspected OceanLotus Campaign
Kaspersky reports a suspected OceanLotus campaign that used malicious PyPI packages to deliver ZiChatBot, turning routine Python installs into a cross-platform backdoor risk.
ClickFix WordPress Attacks Push Vidar Stealer Malware
Australia warns that ClickFix attacks are abusing compromised WordPress sites and fake CAPTCHA prompts to make Windows users run PowerShell commands that install Vidar Stealer.
Fake Claude AI Malware: SectopRAT and Beagle
Fake Claude downloads can lead to SectopRAT or Beagle malware. Check the Artifact, filenames, persistence, cleanup, and account-recovery steps.

GoDaddy ManageWP Phishing Ads Target WordPress Admins
A paid-search phishing campaign is targeting GoDaddy ManageWP logins, turning one stolen dashboard session into a potential multi-site WordPress incident.
Microsoft AiTM Phishing Targeted 35,000 Users
Microsoft says a code-of-conduct phishing campaign targeted 35,000 users with PDF lures, CAPTCHA gates, and AiTM token theft that can bypass ordinary MFA.
CloudZ Malware Abuses Microsoft Phone Link to Steal OTPs
Cisco Talos says CloudZ RAT and its Pheno plugin target Microsoft Phone Link data on infected Windows PCs, turning phone-to-PC syncing into a path toward SMS and OTP exposure.
MuddyWater Uses Microsoft Teams Phishing in Chaos Ransomware Masquerade
Rapid7 says MuddyWater used Microsoft Teams social engineering, remote tools, stolen credentials, and a custom RAT while dressing the intrusion as Chaos ransomware.
Palo Alto PAN-OS Flaw CVE-2026-0300 Exploited for Root RCE
Palo Alto Networks says CVE-2026-0300 is being exploited on exposed PAN-OS User-ID Authentication Portals; the real triage is whether Response Pages expose the portal on an untrusted interface.