If beacon.ser appeared alongside antivirus detections, an unexplained background script, or unauthorized account activity, treat the situation as a possible malware compromise. A malicious beacon can give an attacker a channel back into your computer. Cobalt Strike Beacon is a real remote-access payload that attackers abuse; removing one suspicious file may leave other components behind. Check the security report, scan the whole PC with Gridinsoft Anti-Malware, and secure affected accounts from a clean device. If you suspect remote access is happening now, disconnect the PC from the network first.
Why the beacon.ser report matters
In a Reddit account of a home-PC infection, the user described a background script, a threat they called beacon.ser, an antivirus scan that found 17 threats, and unauthorized purchases on two payment cards. [1] The important point is the combination: suspicious execution, multiple detections, and financial account misuse. That calls for system cleanup and account recovery, rather than simply finding an application that opens a SER file.
The post does not include a file hash or a detailed detection report that identifies the sample as Cobalt Strike. It is a report of a serious incident, but it cannot establish the exact malware family or how the card details were obtained. The response below covers the security problem without inventing those missing findings.
What is a Beacon Trojan, and how does Cobalt Strike fit?
Beaconing is the communication between an infected computer and an attacker’s command-and-control server, often shortened to C2. Think of it as the compromised device checking in, waiting for instructions, and sending results back. The connection gives the attacker a way to keep using access after the initial infection.
Beacon is also the name of Cobalt Strike’s post-exploitation payload. Cobalt Strike is a commercial security-testing tool; when criminals deploy its Beacon without authorization, they can use that foothold to carry out further malicious activity. Fortra documents communication over HTTP/HTTPS and DNS, as well as linked Beacon connections. Check-ins can be delayed or varied, so a beacon does not have to contact its server at perfectly regular intervals. [2]
This is a serious threat category. In documented attacks, Cobalt Strike has been used alongside credential theft and ransomware deployment. [4] Our earlier report on fake exploits delivering Cobalt Strike Beacons shows one delivery scenario. It does not mean every file containing the word beacon is that payload.
Check what the security warning actually says
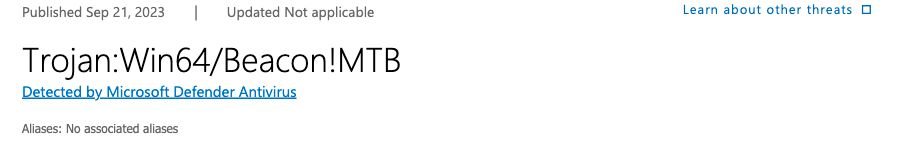
Start with the full detection name, affected path, time, and action taken. Microsoft lists Trojan:Win64/Beacon!MTB as a threat capable of performing actions chosen by a malicious actor. Its guidance also notes that infections can leave files and system changes requiring further scanning. [3]
- Active, running, or action needed: contain the device and complete cleanup promptly. Record the alert before dismissing it.
- Quarantined or blocked: the tool has taken a protective action. Check whether the file was blocked before execution and whether there are other detections. An old quarantined event does not by itself show that a backdoor is still running.
- Repeated outbound-connection warnings: record the process, destination, and timestamps. A file or process repeatedly trying to reach a malicious server needs investigation even after one item was removed.
- A filename with no detection: establish its origin and scan it. The filename is a lead, not a substitute for a security report.
A warning shown only inside a web page, especially one demanding a telephone call or payment, is different from a detection in your installed antivirus. Open the security application directly to check its history.
What to do first if you suspect an active infection
- Disconnect the affected PC. Turn off Wi-Fi and unplug Ethernet if there are signs of active remote access, continuing malicious connections, or account abuse associated with the incident.
- Stop sensitive activity on it. Do not use that PC for banking, email recovery, shopping, password changes, or signing into a password manager.
- Save the useful evidence. Record detection names, paths, timestamps, scan results, and suspicious transactions. Do not restore quarantined malware to make a screenshot or upload it.
- Use a clean device for account recovery. Secure affected accounts and contact the relevant service or card issuer through its official app, website, or known contact number.
- For a work computer, contact IT or security. They may need to preserve memory and logs before a restart or reinstallation. Do not reconnect it to a company network just to see whether the problem returns.
How to check the suspicious file without running it
File checks help identify what was detected and where it came from. Do not delay containment or a full scan to finish every optional check.
Confirm the full name, path, and source
In Windows 11 File Explorer, select View → Show → File name extensions. A file named beacon.ser.exe is an executable with a misleading extra suffix. A file ending in .ser may contain serialized Java data or application-specific content. That does not make it safe: a malicious component can load data from another file.
Record the complete path, such as %USERPROFILE%\Downloads\beacon.ser, and compare its appearance with recent downloads, installers, scripts, or antivirus events. A file in AppData or Temp is not automatically malware, but an unknown program recreating a detected file there deserves a system-wide check. If the actual item is an EXE, use the source and signature checks for Windows executables.
Calculate a hash if support needs the exact file
A SHA-256 hash distinguishes your file from another one with the same name. If the file is accessible and not quarantined, open PowerShell and replace the example location with its actual path:
$filePath = Join-Path `
  $env:USERPROFILE `
  'Downloads\beacon.ser'

Get-FileHash `
  -LiteralPath $filePath `
  -Algorithm SHA256
This reads the file without launching it. Send the hash and detection details to support when requested. A hash lookup with no existing report is not a clean result. For private application data, use a local scan rather than uploading the whole file to an unknown service; see our private-file scanning guide.
Inspect the header only when it helps identification
This optional command uses the same $filePath variable to display the first row of raw bytes:
Format-Hex `
  -LiteralPath $filePath |
  Select-Object -First 1
A beginning of AC ED 00 05 matches the standard Java serialization header. [5] That identifies a possible data format, not the file’s trustworthiness. Do not feed an unknown file into a Java deserializer or rename it to EXE to test it. If the bytes do not match, preserve the file’s identity and ask for analysis instead of guessing a format. Leave quarantined files quarantined.
Scan and clean the PC with Gridinsoft Anti-Malware
For a suspected Beacon infection, checking only beacon.ser is not enough. The initial loader, another downloaded payload, a startup component, a service, a scheduled task, or a browser change may remain after the visible file is removed. A full-PC scan is the practical next step.
- Obtain Gridinsoft Anti-Malware from its official download. The button below opens the official installer. If the affected PC is isolated because you suspect active remote access, use a clean device or your IT team to obtain the tool; limit any necessary reconnection to the installation/update work.
- Install it and update the malware databases. Use current definitions before evaluating the system.
- Run a Full Scan. Check the whole PC, rather than scanning only the one named file or its Downloads folder.
- Review the detections and apply cleanup. Keep the report. If an expected application is flagged and you suspect a false positive, give support the exact detection and hash instead of disabling protection or restoring it blindly.
- Restart when prompted, then recheck. Confirm whether the same alert, suspicious file, background script, or blocked connection returns. Save a new scan result if it does.
The scan and cleanup workflow does not require you to delete services, scheduled tasks, or registry entries manually. If the problem returns, those become targeted follow-up checks for support or an analyst. A clean result is useful evidence; it cannot establish that an attacker never accessed an account or copied data before cleanup.
What if the file or connection keeps returning?
A returning detection can mean a loader, startup mechanism, or another compromised component is recreating the file. It can also be a repeat scan of the same archive or an old history entry. Compare the new timestamp, affected path, process, and action before deciding which situation you have.
The letters ser do not establish that malware installed a Windows service. To investigate service-based persistence, an analyst needs the actual service name, executable path, startup setting, and evidence linking it to the detection. Services are only one possible startup mechanism. Do not disable unfamiliar Windows services at random or delete a legitimate host process.
Keep the PC isolated if new suspicious connections continue. Provide support with the scan report and recurrence details. If unauthorized administrator access is confirmed, malicious changes remain unexplained, or sensitive work is involved, consider a clean Windows installation with professional assistance. Preserve needed evidence first, and do not restore the suspicious installer or unverified system image. A separately named alert such as MODBEACON needs its own family-specific investigation.
What could have been exposed?
The danger of an unauthorized beacon is what an attacker can do through the access: run commands, collect information, install additional malware, steal credentials or files, and potentially deploy ransomware. CISA’s Ghost/Cring advisory documents attackers using Cobalt Strike for credential access and progressing to ransomware. [4] These are possible consequences of a compromise, not findings established for every Beacon alert.
If the incident includes unfamiliar sign-ins, card charges, or account changes, take these steps from a clean device:
- Secure your main email account. Change its password, review recovery settings and forwarding rules, and sign out unfamiliar sessions.
- Secure affected financial and other accounts. Replace exposed or reused passwords with unique ones and enable multifactor authentication where available.
- Revoke active sessions and suspicious access. A password change alone may not address every existing session or connected application.
- Contact the card issuer or service promptly. Report transactions or account actions you did not authorize, ask about protective steps, and retain your reports. Malware cleanup does not reverse a transaction or guarantee reimbursement.
Removing a backdoor closes one part of the incident. Restoring control of accounts and checking what happened while the attacker had access is a separate part.
FAQ
Is beacon.ser definitely Cobalt Strike?
The filename alone cannot establish that. Cobalt Strike Beacon is a real threat when deployed by an attacker, but attributing a particular file requires a detection report or analysis. In the Reddit case, the reported threats and account misuse warrant action even though the exact family remains unverified.
Does a Beacon alert mean the attacker is connected right now?
Check the event status and time. An active process or continuing malicious outbound traffic demands containment. A file blocked before execution or an old quarantined item is a different situation. Investigate associated detections and scan the system rather than assuming either live access or complete safety.
Can deleting beacon.ser remove the whole infection?
Deleting one file may leave its loader or another persistence mechanism behind. Use the Full Scan, cleanup, restart, and symptom-recheck workflow. If it reappears, give support the fresh event details instead of repeatedly deleting the same filename.
Should I open it in Windows Sandbox to see what happens?
Do not run or deserialize a detected file out of curiosity. A quiet test cannot establish that the PC was never compromised or that an account is secure. Our Windows Sandbox safety guide explains those testing limits.
References
- Reddit, r/BankOfAmerica. “Advice on fighting fraud claim – BoA credit card.” User-reported incident, accessed November 5, 2026. Original user report.
- Fortra. “Cobalt Strike Beacon.” Cobalt Strike product documentation, accessed November 5, 2026. Beacon payload and communication.
- Microsoft Security Intelligence. “Trojan:Win64/Beacon!MTB.” Published September 21, 2023; accessed November 5, 2026. Threat description and cleanup guidance.
- FBI, CISA, and MS-ISAC. “#StopRansomware: Ghost (Cring) Ransomware.” Advisory AA25-050A, February 19, 2025; accessed November 5, 2026. Documented Cobalt Strike abuse.
- Oracle. “Object Serialization Stream Protocol.” Java Object Serialization Specification, Java SE 25, section 6.4.2; accessed November 5, 2026. Java stream-header constants.