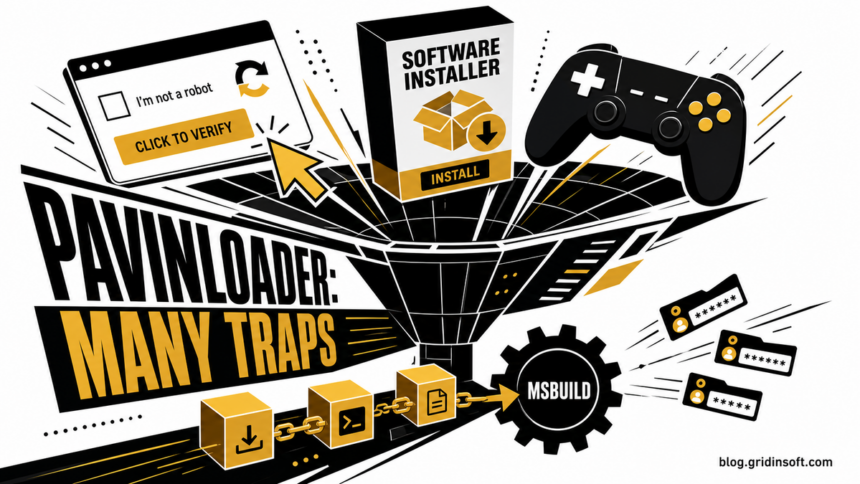
Malwarebytes researchers have identified PavinLoader in several Windows infection campaigns that begin with different lures: fake CAPTCHA instructions, counterfeit software downloads, and malicious Ren’Py game installers. Seeing one of those pages is not itself an infection. The serious exposure starts when a user runs the copied command, installer, or game package, allowing a multi-stage chain to abuse MSBuild, load trojanized .NET components, find its server through EtherHiding, and deliver Amatera Stealer or another payload.
The name matters because PavinLoader is no longer tied to one fake-game campaign. The same technical pattern now connects several delivery routes. Malwarebytes says the shared artifacts suggest the loader could be offered as a service, but the researchers did not find a sales channel or build panel and therefore do not confirm a Loader-as-a-Service operation.
How users encounter PavinLoader
- Fake CAPTCHA or ClickFix page: the page tells the visitor to copy and run a Windows command. The checkbox or page view is not the compromise boundary; executing the command is.
- Fake software download: the user receives an MSI or another installer that appears to belong to a legitimate program. Downloading it creates a file risk, while running it starts the observed chain.
- Malicious game or Ren’Py package: a game can appear to open normally while its bundled loader runs in the background. Our RenPy Loader recovery guide covers this specific branch in more detail.
Those entry points should not be treated as one universal sample. Filenames, folders, intermediate files, and final malware can change between builds. PavinLoader is the common loader pattern, not proof that every victim received the same Amatera payload.
What happens after execution
- The lure launches an MSI, BAT/CMD file, MSBuild project, or another first-stage component.
- A legitimate Windows build tool is used to load code from a trojanized or custom .NET DLL. Observed DLL bases included DotNetZip, Nancy, Renci.SshNet, and OpenXML.
- An EtherHiding stage queries a blockchain contract to recover the current command-server domain instead of storing one fixed address in the first file.
- The loader performs anti-analysis checks and retrieves later stages from that server.
- A PE loader starts the final payload. Malwarebytes recovered Amatera Stealer in the analyzed Ren’Py chain and observed other malware in additional infections.
EtherHiding does not put the malware itself “on the blockchain.” It gives the chain a replaceable pointer to attacker infrastructure. That distinction is useful during triage: blocking one domain may interrupt a current build, but it does not remove the files that already ran or prevent the contract from pointing later builds elsewhere.
PavinLoader clues worth checking
No single filename proves a PavinLoader infection. The stronger signal is a relationship between the lure, an unusual execution path, Windows build tooling, and the following network activity. Malwarebytes documented several recurring patterns:
.bat,.cmd,.csproj, MSI, and EXE files with short or generated-looking names;- a copied or renamed MSBuild executable launched from a user-writable folder rather than its normal Windows framework path;
- trojanized .NET libraries with inserted methods that often follow a two-word or two-word-plus-number naming pattern;
- HTTP requests for JSON paths built from two random words, after a blockchain RPC request resolves the current server;
- later infrastructure using rotating domains, commonly under
.lat,.icu,.shop, or.cfd.
These are investigation leads, not safe-delete rules. Legitimate software also uses MSBuild, DLLs, MSI packages, and some of those top-level domains. Check the parent process, original download, full path, creation time, signature, and network sequence together. If MSBuild.exe itself looks suspicious, use the MSBuild safety checklist before removing a legitimate Windows component.
What to do after a PavinLoader lure
- If you only saw the page, close it. Do not paste its command, download its proposed “fix,” or approve an installer. A normal CAPTCHA never needs Windows Run, PowerShell, Terminal, or Command Prompt.
- If you downloaded but did not run the file, keep it closed. Record the source URL and filename, delete or quarantine the download, and scan it without executing it.
- If you ran the command or installer, disconnect the PC. Turn off Wi-Fi or unplug Ethernet. Do not sign in to email, banking, crypto, gaming, or work services from the suspect computer.
- Secure accounts now from a separate trusted device. Do not wait for the PC scan to finish. Start with email and the password manager: change exposed passwords, check recovery email/phone and MFA settings, remove unfamiliar access, revoke active sessions, and replace exposed recovery codes. Then secure other accounts and work credentials available on the PC; contact your IT team for a work device. The password-stealer response guide covers session, token, and wallet exposure. Keep using the clean device while PC cleanup proceeds.
- Preserve the useful trail. Save the approximate execution time, download URL, filename, browser history entry, security alerts, and any command visible in the page. Do not run the sample again or delay urgent account protection to collect logs.
- Clean the suspect PC. Download and install Gridinsoft Anti-Malware from its official site, update its detection database, and run a Full Scan. Review the detections, apply the recommended removal or quarantine actions, and restart when requested. Keep the PC offline except for the connection needed to obtain or update the scanner; do not use that connection to sign into accounts. If malware prevents installation or scanning, seek help with Safe Mode or offline recovery, then return to the full scan.
Deleting the original MSI, BAT file, or game folder is not enough after execution. A downloaded loader or stealer may remain in the user profile, temporary folders, startup entries, scheduled tasks, services, or browser data. A full scan helps check for these leftovers; it does not revoke stolen sessions or recover exposed credentials. Investigate security exclusions or unusual .NET/MSBuild files with an expert if activity continues, rather than deleting legitimate Windows components by name.
Keep the suspect PC out of your accounts. Secure email, revoke sessions, and change exposed passwords now from a separate trusted device while you clean this Windows PC. Scan for remaining malware before signing in here again.
Scan for PavinLoader leftoversIf the infection began with a copied command, compare the event with our ClickFix execution and account-recovery checklist. That page covers the same critical boundary: viewing a lure is different from running the command it supplies.
PavinLoader detected again after cleanup
A later detection can reflect a broader scan or updated detection rules finding an older file. It can also indicate something that survived cleanup or recreated the file. The detection name alone does not distinguish these situations.
- Compare the reports. Save each scan’s time, scan type/scope, detection name, full affected path or resource, and action status. Check whether the alert is a new event or an old history entry, and whether remediation succeeded, failed, or is still pending.
- Identify what was found. An item already isolated in quarantine or an unopened installer/archive is different from a newly created task, a running component, or a file that reappears after removal. Do not restore a detection or reopen the download to test it. A leftover file still needs handling, but its presence alone does not establish active persistence.
- Remediate, restart, and compare a fresh scan. Complete the selected cleanup actions and rerun a Full Scan with current definitions. Note whether the same resource returns with a new event time and whether the original symptoms continue.
If new detections continue, remediation fails, or suspicious processes or connections return, keep the PC isolated and take the reports to a qualified malware-removal specialist or your IT team. If its integrity cannot be established, a clean Windows reinstall from official media may be appropriate; preserve needed documents and avoid restoring suspect installers or scripts. Clean follow-up scans do not undo account theft, so continue recovery from the separate trusted device.
References
- Gabriele Orini. “Tracking PavinLoader across ClickFix and fake download campaigns.” Malwarebytes Threat Intel, August 24, 2026. Primary technical analysis.
- Google. “Secure a hacked or compromised Google Account.” Google Account Help, accessed October 14, 2026. Account recovery and security checks.