CVE-2026-53412: Update Zoom for Windows to Block Account Takeover
CVE-2026-53412 is a critical Zoom Workplace for Windows flaw that may allow unauthenticated account takeover. Check your version and update now.

mdnsNSP.dll Blocked by Local Security Authority: Safe Fix
Windows blocked mdnsNSP.dll from Local Security Authority? Check the Bonjour path and signature, then update, repair, uninstall, or scan safely.
How to Block Remote Access Scam Software on Windows
Protect a family Windows PC from remote-access scams with a standard account, SmartScreen, Store-only apps, and safely tested AppLocker rules.

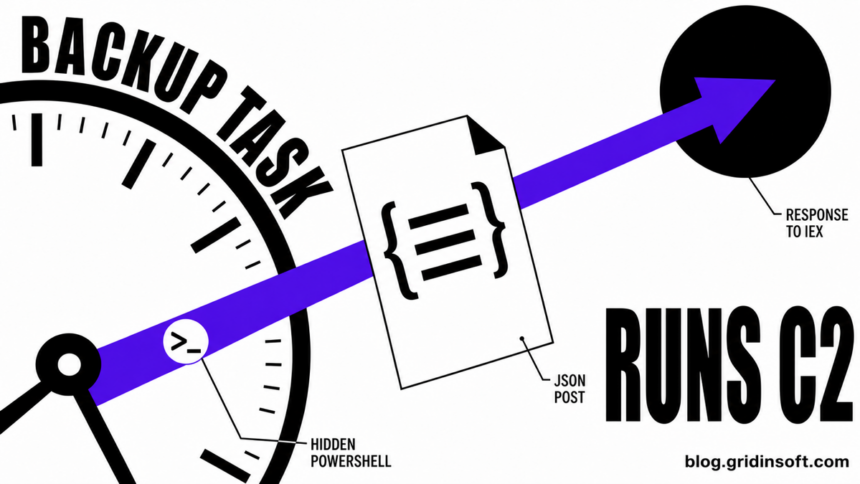
OkoBot/TookPS: New C2 and GDrive Backup Sync Task
Gridinsoft Labs identifies 22tuk.digital as a new high-confidence TookPS/OkoBot callback and analyzes its encoded PowerShell launcher, JSON protocol, scheduled task, and reverse SSH indicators.

sppsvc.exe: Safe Windows Service, High CPU, or Malware?
Is sppsvc.exe safe? Check its System32 path and Microsoft signature, fix high CPU or activation errors, and respond safely to Expiro alerts.
Trojan:Win32/BypassUAC!rfn: Meaning and Removal
Defender found Trojan:Win32/BypassUAC!rfn? Check the affected path, quarantine status, false-positive signals, recurring alerts, and safe removal steps.
Cursor git.exe Flaw: Check Windows Repositories Before Opening
A disclosed Cursor flaw can run a repository-local git.exe on Windows when a project opens. Check the root folder and recover safely after exposure.
Fake LastPass and Bitwarden Security Emails Push Downloads
Fake LastPass and Bitwarden security-policy emails use newsletter and compliance lookalike domains. Check the sender, avoid the download, and secure your vault.
CapabilityAccessManager.db-wal Huge? Fix Windows 11 Disk Use
Is CapabilityAccessManager.db-wal filling your Windows 11 C: drive? Confirm the path, install KB5101650, stop recurrence, and reclaim space safely.
LabubaRAT Malware: Check and Remove the Fake NVIDIA RAT
LabubaRAT malware hides as nvidia-sysruntime.exe. Verify its signature and hash, remove autorun, scan for leftovers, and secure exposed accounts.
MODBEACON RAT: Removal, Persistence, and Fake Installer Checks
MODBEACON RAT hides behind counterfeit installers and can persist through WMI, tasks, or services. Follow safe containment, removal, and recovery steps.
PAXOS Token Launch Scam: Fake $PAXOS Wallet Trap
The fake $PAXOS Token Launch at paxolaunch.live targets PAX Gold holders with a wallet-connect trap. Learn the warning signs and recovery steps.