

PUABundler:Win32/Rostpay: What It Is and How to Remove It
Defender flagged PUABundler:Win32/Rostpay? Learn what it means, why DriverHub or Tesla Browser…

WerFault.exe Application Error Fix
WerFault.exe application error usually means another app or driver is crashing. Check…
PUA:Win32/GameHack: Remove It or False Positive?
Defender found PUA:Win32/GameHack? Use the affected file path to decide false positive…
How to Disable Windows Defender on Windows 11 Safely
Need to disable Windows Defender on Windows 11? Use Windows Security for…
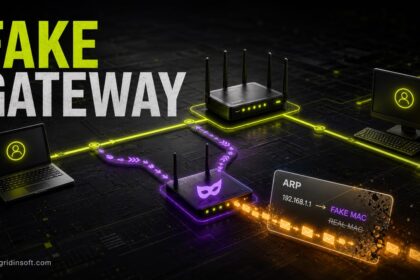
ARP Spoofing Attacks: Detection, Prevention, and False Alerts in 2026
Learn how ARP spoofing works, how to check ARP cache poisoning alerts,…
Trojan:Script/Downloader!MSR: Meaning and Removal Guide
Trojan:Script/Downloader!MSR is a Microsoft Defender alert for a script that can download…
Trojan:Win32/Malgent!MSR: Removal & False Positive Checks
Check what a Malgent warning means, whether the detected file ran, and…
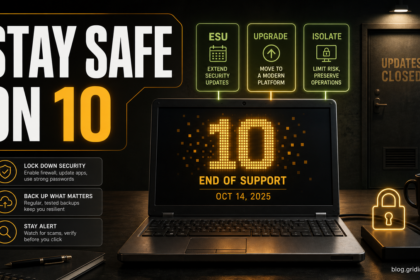
Secure Windows 10 After End of Support: What to Do in 2026
Still using Windows 10 after support ended? Learn when to use ESU,…
Trojan:Win32/Tnega!MSR: False Positive or Remove It?
Seeing Trojan:Win32/Tnega!MSR? Check the affected path, source, signature, false-positive clues, and safe…
Virus:Win32/Floxif.H Removal
Virus:Win32/Floxif.H is a severe Microsoft Defender file-infector alert. Learn how to remove…
PUA:Win32/Presenoker: Meaning, Removal, and Safe Check
PUA:Win32/Presenoker is a Microsoft Defender detection for a potentially unwanted application, not…
Trojan:Win32/Wacatac.H!ml: False Positive or Remove?
Defender found Trojan:Win32/Wacatac.H!ml? Check the path and source, decide restore vs remove,…