Matrixgrowthforge.com Ads: Remove Browser Notifications
Seeing Matrixgrowthforge.com ads or fake browser notifications? Remove the permission, check extensions and startup items, and scan if pop-ups return.

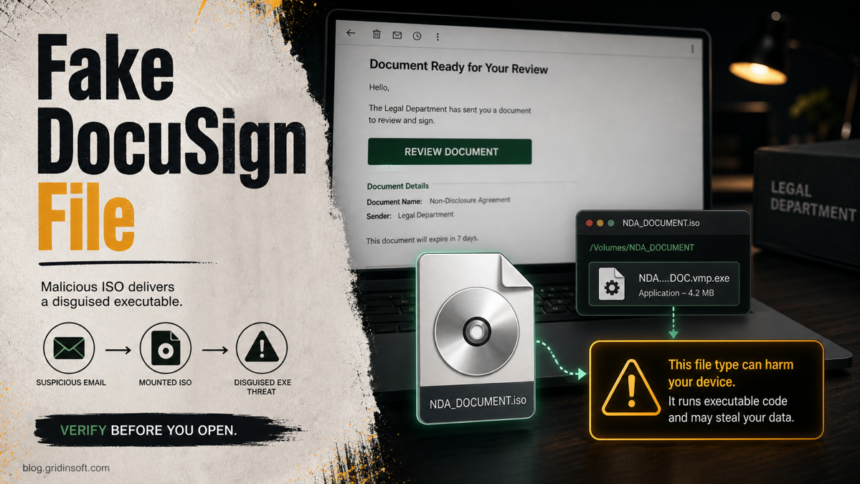
DocuSign Legal Department Document Email Virus
A fake DocuSign Legal Department email delivers an ISO with a disguised executable. Learn how to verify the request safely and what to do if you opened it.
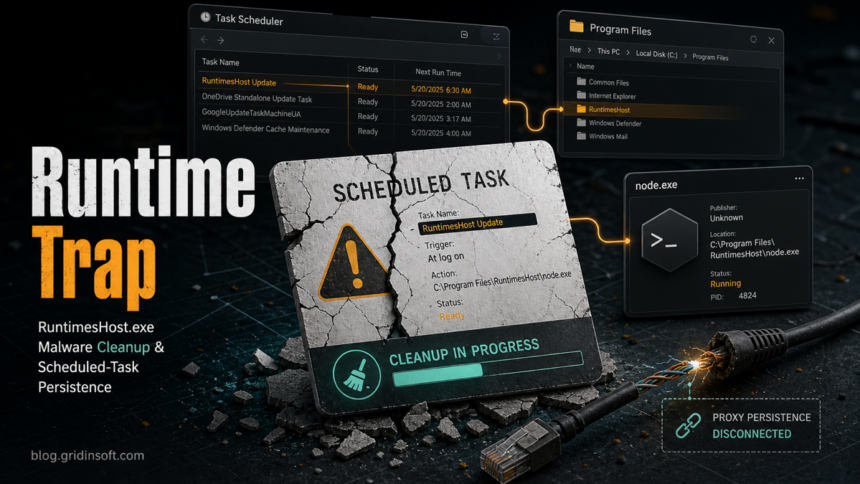
RuntimesHost.exe Virus Cleanup
Found RuntimesHost.exe, node.exe, or a RuntimesHost_user task? Learn what it means, how to remove proxy malware persistence, and when to scan or change passwords.

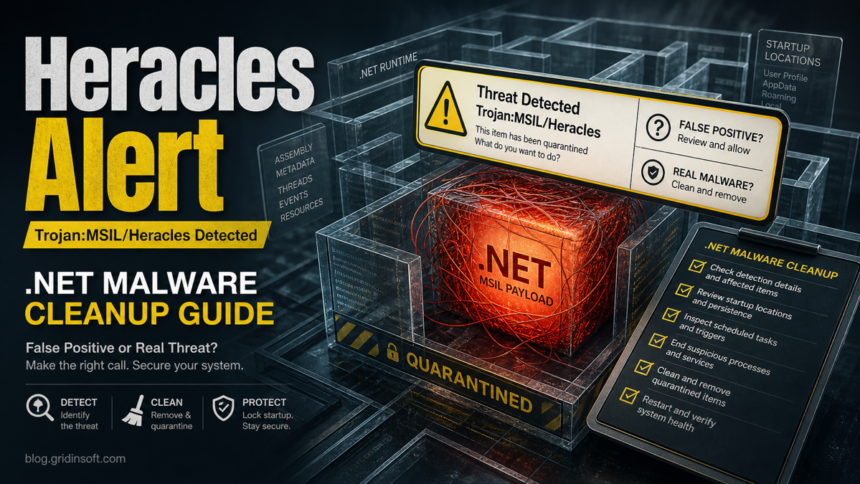
Trojan:MSIL/Heracles: Defender Alert and Cleanup
Seeing Trojan:MSIL/Heracles or a Heracles !MTB variant in Microsoft Defender? Check the source, false-positive signals, recurrence, and safe cleanup steps.
Gen:Variant Detection: False Positive or Malware?
Gen:Variant alerts from Bitdefender, Emsisoft, and related engines need source, path, signature, and scanner-context checks before you restore or delete the file.
Clean Scan Popups
Windows Defender says no threats found but threat popups keep appearing? Separate real Protection History alerts, stale notices, browser fake alerts, and recurring malware.
Trojan:Win32/Caynamer.A!ml: False Positive or Malware?
Seeing Trojan:Win32/Caynamer.A!ml in Microsoft Defender? Learn when to remove it, when a developer or game file may be a false positive, and what to check before restore.
Win32:Evo-gen[Trj]: False Positive or Malware?
Win32:Evo-gen[Trj] is an Avast/AVG heuristic alert. Learn when it is likely a false positive, when to remove the file, and how to check it safely.
Estart Center / E START App Removal After CrystalDiskInfo
Estart Center or E START App appeared after CrystalDiskInfo? Uninstall the bundle, restart Windows, check startup/browser leftovers, and scan if pop-ups return.
Trojan:Win32/Egairtigado!rfn
Defender found Trojan:Win32/Egairtigado!rfn? Check the affected path, WinRAR Default.SFX context, false-positive signs, and cleanup steps before restoring the file.
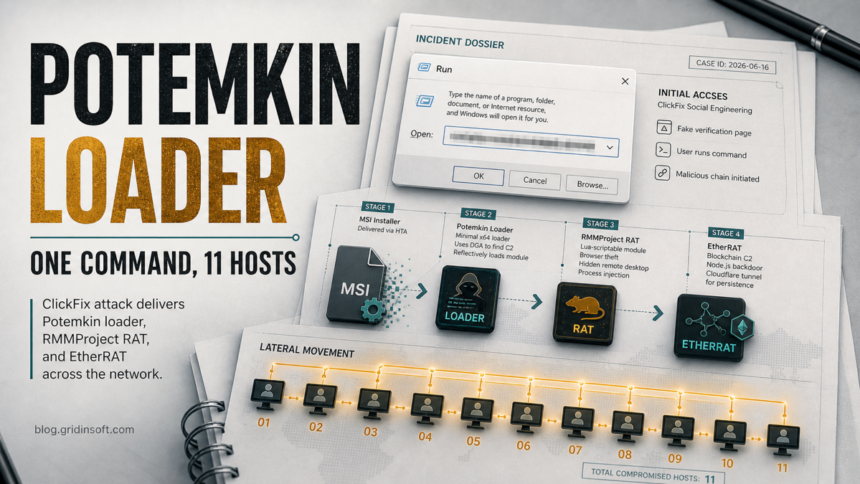
Potemkin Loader Turns ClickFix Into 11-Host Intrusion
A ClickFix command dropped Potemkin Loader, RMMProject and EtherRAT across 11+ hosts. Here is what to check after a fake verification command ran.
Malware.AI Detection: False Positive or Malware?
Malware.AI is a Malwarebytes machine-learning detection. Learn when it may be a false positive, when to remove it, and how to check game files safely.