Pdftools.store Redirect Removal: Clean ipqcr.pdftools.store
Remove pdftools.store and ipqcr.pdftools.store redirects from Chrome or Edge. Clean extensions, search settings, notifications, policies, and adware.

Five Eyes AI Risk Checklist
Five Eyes warns that AI is shrinking patch windows. Use this practical checklist for patching, suspicious downloads, account security, and malware cleanup.

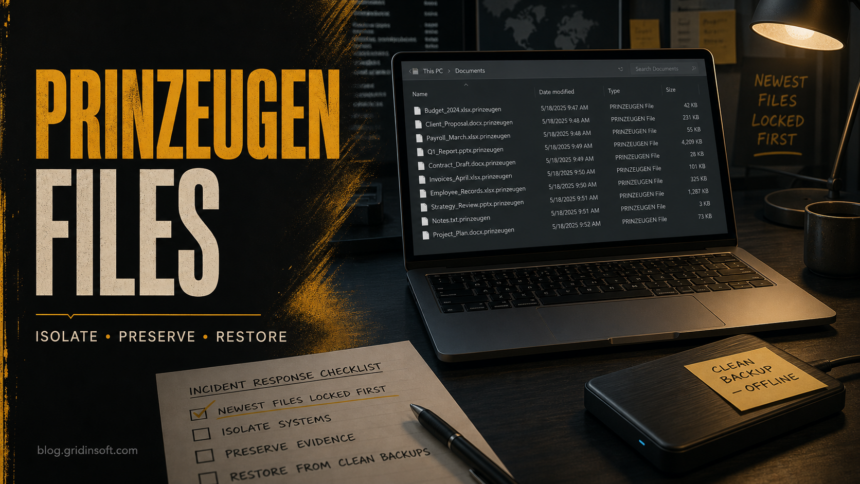
Prinz Eugen Ransomware: .prinzeugen File Recovery Guide
Prinz Eugen ransomware appends the .prinzeugen extension and may leave no ransom note. Learn how to isolate the PC, preserve evidence, check safe decryptor options, clean malware, and restore from…
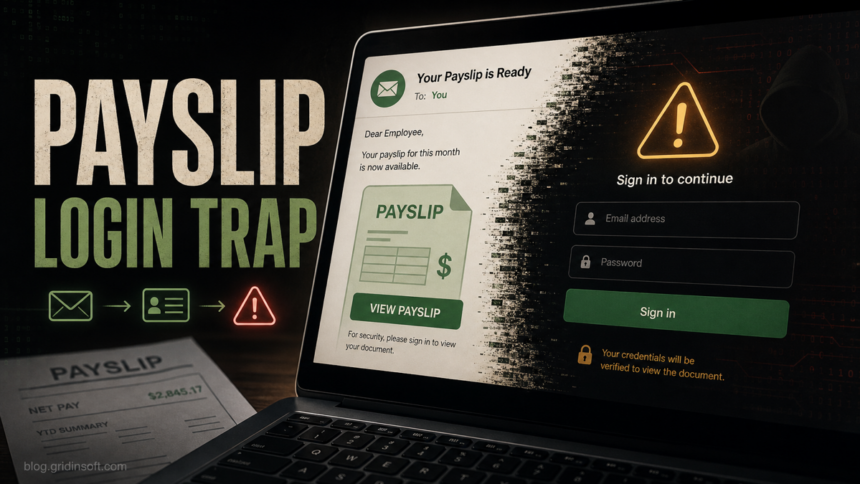
Your Payslip Is Available Email Scam
Fake payslip, Payroll File Shared, and Important Payroll Update emails can lead to credential theft or payroll diversion. Learn how to verify them and recover safely.

TokenSight TKST Airdrop Scam: tkstio.pages.dev Wallet Drain Trap
The TokenSight TKST Airdrop page at tkstio.pages.dev is a fake wallet-drainer lure. Learn the warning signs and what to do after connecting a wallet.
Pureextension.net Redirect: Remove the Pure Safety Hijacker
Pureextension.net redirect changed your browser search or new tab? Remove the Pure Safety extension, check browser policies, reset search settings, and scan adware leftovers.
OXLOADER Malware: Fake Node.js Ads Drop CastleStealer
A fake Node.js sponsored result delivered OXLOADER and CastleStealer. Learn what to check after a suspicious installer and how to protect accounts.
Paint.NET Virus Cleanup
If a Paint.NET download led to pop-ups, a lock screen, or a suspicious installer, use this guide to tell the real app from a fake download and clean Windows leftovers…
AUEPDU.exe Alert
AUEPDU.exe is usually tied to AMD telemetry, but Bitdefender or AT&T blocked URL alerts still need file, signature, and network triage before you allow anything.
PDFixers.exe Alert: Cleanup Guide
Saw PDFixers.exe, PDFixers App, or a pdfixers.com block? Use the triage map, remove leftovers, and scan with Gridinsoft before restoring anything.
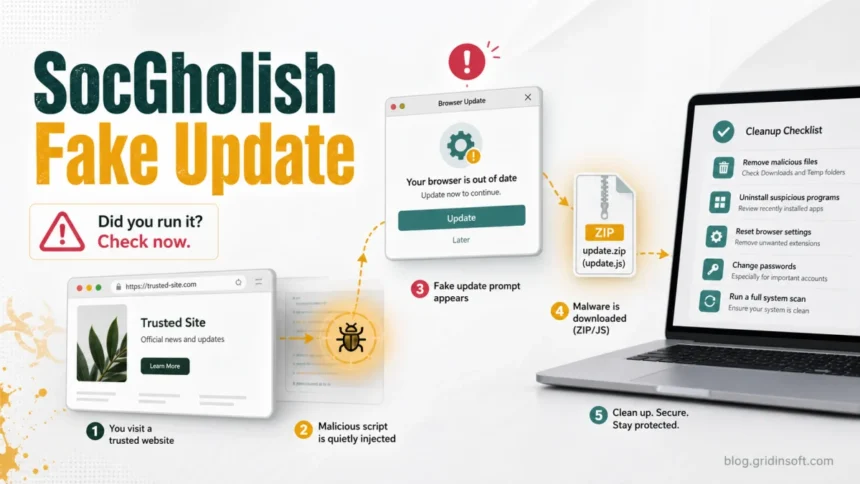
SocGholish Malware: Fake Update Removal Guide
SocGholish, also called FakeUpdates, uses fake browser update prompts on compromised sites. Learn what to do if you downloaded or ran the fake update.
Trojan:Win32/WinLNK.CLL!MTB
Defender detected Trojan:Win32/WinLNK.CLL!MTB in a recovery package? Check the path, scan status, false-positive signs, and safe cleanup order.