

Storm-2570 Uses Four Ransomware Brands—and the Same Access Tools
Microsoft links Storm-2570 to four ransomware families. Repeated remote access, credential theft…

CLOSEDQUORUM: Windows Malware Puts Its Next Move to a Vote
Talos found a Windows implant designed to take votes from four AI…
Trojan:PowerShell/Boxter!MTB: Remove It and Check Repeat Alerts
Check a Trojan:PowerShell/Boxter!MTB alert, remove detected threats, and distinguish new PowerShell activity…
AWS Quarantined a Leaked Key in 10 Seconds. The Response Wasn’t Over.
Unit 42 measured AWS quarantining a public GitHub key leak in 10…
Diagnostic Policy Service High CPU: Find What Keeps It Busy
Trace Diagnostic Policy Service CPU spikes to their trigger. Check the host…
Service Host Network Service High Network Usage: Find the Download
Identify the service behind heavy Windows network traffic, separate downloads from peer…
State Repository Service High CPU: Find the App Behind It
Trace State Repository Service high CPU to an app, update or Windows…
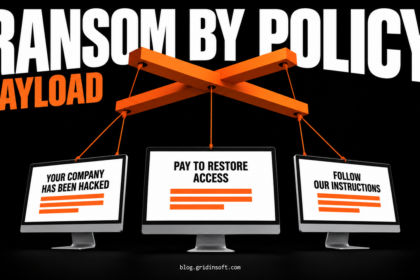
PAYLOAD Turns Windows Group Policy Into a Ransom Demand
PAYLOAD attackers used domain policy to display ransom notes without encrypting Windows…
Three Exploited Linux Kernel Flaws: Check Your Patch Track
CISA lists three exploited Linux kernel flaws. Check the exact Ubuntu kernel…
AgentCore Harness Test Exposes a Service Token Through Memory
Unit 42 demonstrated AgentCore credential theft through a support ticket. See why…
LeakySensey Rents Out Hacked Routers as a Proxy Network
LeakySensey turned weak VPN logins into rented proxies. What the exposed server…
Settra Ransomware Leaves a Defender Log Intact After a Typo
Huntress found that Settra misspelled a Defender event-log name. What survived, how…