A Linux administrator could type a password, see the requested command run normally, and still hand the password to an intruder. In a newly published investigation, Unit 42 describes attackers who changed the shell’s startup file to intercept sudo before passing the captured password to the real command. That small detour was part of a wider campaign against government and state-affiliated infrastructure.
The October 15 report tracks the activity as CL-UNK-1211, observed between October 2025 and April 2026. The toolkit included PHP backdoors, a custom remote-access Trojan called SysGoRAT, and scripts searching government mailboxes for social-media messages. Researchers found signs of AI-assisted script creation, but the evidence does not establish that an autonomous agent ran the campaign or identify a sponsoring state.
The password prompt that kept the command working
The attackers modified .bashrc, a configuration file used when starting interactive Bash sessions. They installed an alias: a shell-level replacement that intercepted the familiar command name sudo. Instead of immediately reaching the legitimate privilege-management program, the user encountered the attackers’ password prompt.
The replacement collected the password, wrote it to a log, and then supplied it to the real sudo command. The requested operation could therefore continue. Successful authentication was part of the concealment. A familiar prompt and a working command did not show who handled the password first.
The stolen credentials went into Solarwinds.StatusLog.txt, a name chosen to resemble ordinary software activity. Unit 42 explicitly says it found no evidence that SolarWinds infrastructure was compromised. The label was camouflage, not attribution.

This is a modification of an already accessed environment, not evidence that every Linux installation has a new sudo vulnerability. For administrators investigating a suspect server, shell aliases and startup-file changes belong alongside executable integrity checks. Merely verifying that the genuine sudo binary exists would miss the interception described here.
A backdoor loaded before the website’s own PHP
The intrusion also reached beyond individual web-shell files. Attackers changed auto_prepend_file settings across PHP configurations under /etc/php/ and /opt/plesk/php/. PHP uses this setting to load a designated file before executing the requested script. In the reported case, the designated file was a malicious web shell at /usr/lib/php/plesk_sys_driver.php.
That configuration explains why a clean-looking page is an incomplete check: code can run before the page’s own script. The setting itself has legitimate uses; the investigative question is whether its effective value and referenced file match the server’s approved configuration. Unit 42 also found a credential logger inserted into a PHP login page and searches for email, SMTP and database passwords in configuration files and shell history.
A separate access route used SysGoRAT, a Go-based remote-access Trojan supporting Windows and Linux. Its capabilities included command execution, interactive shells, file access and proxying connections through the infected host. Operators renamed the binary to blend into the environment. A plausible filename was therefore a weak basis for clearing it.
Government email became a map of social accounts
The mailbox search had a more specific purpose than collecting arbitrary documents. Attackers enumerated mail directories, then used a PHP script named search_social.php to find messages associated with social platforms. Its output exposed the message’s path, sender, recipient and subject.
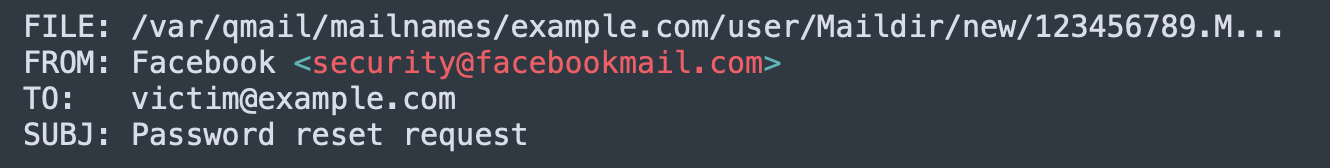
The implication is a second trust boundary: access to a mail server can reveal which external accounts use those addresses and where account-recovery messages arrive. This investigation describes an attempt to exploit that relationship; it does not establish that every account located through the search was taken over.
Nor did every tool work. One attempted mailbox-archiving script, zip_mails.sh, contained syntax errors and would fail as written. That failure limits what the specific artifact proves. It does not cancel the other observed credential theft, backdoors or data-access attempts.
AI clues did not make the attackers invisible
Researchers found conversational comments and step-by-step reasoning inside deployed scripts, consistent with code copied from language-model output or used by an AI agent. Those artifacts support AI assistance; they do not distinguish reliably between an operator pasting generated code and an autonomous system directing the intrusion.
The attackers also attempted to erase logs, alter file timestamps and plant references to a penetration test. Their attempts to terminate Cortex XDR processes were detected and mitigated, according to Unit 42. Neither a missing local log nor an old-looking file timestamp is strong reassurance in a case where deleting and disguising evidence was part of the operation.
The useful response follows those access paths: preserve available evidence, inspect shell startup files and effective PHP configuration, and assess the credentials and mail-linked accounts exposed from the affected host. Perform sensitive recovery from a trusted environment; changing a password through an intercepted prompt can disclose the replacement too. This is a server-investigation problem, rather than a reason to install a Windows cleanup tool on Linux. Earlier BPFDoor and AVERAT research on mail gateways describes a separate campaign with a related visibility challenge.
References
- Roey Porat and Tom Fakterman. AI-Powered Espionage Campaign Targets Government Linux Infrastructure. Unit 42, Palo Alto Networks, October 15, 2026.
- PHP Documentation Group. Core php.ini directives: auto_prepend_file. PHP Manual. Accessed October 16, 2026.