A verified HBO Max account on Reddit became the front door to a malware operation: researchers counted 108 malicious ads in roughly 48 hours, with lures ranging from a supposed streaming app to developer tools. The consequential step happened after the click, when a download page asked the visitor to paste a command into Terminal.
A September 13 report from ADAMnetworks, based on joint research with Hudson Rock, follows that advertising campaign into a broader operation called PasteSwitch. Its revealing feature is how much can change behind the same instruction: the brand, destination and malware can rotate while the victim still supplies the final act of execution.
The real account made the fake download credible
The investigators trace the initial report to a Reddit user who saw an ad from the verified u/hbomax account. It promoted an HBO Max application for macOS and sent visitors to hbomaxx[.]us, a page dressed in the service’s branding. The copied identity was credible enough to make a software download look like a normal extension of a familiar subscription.
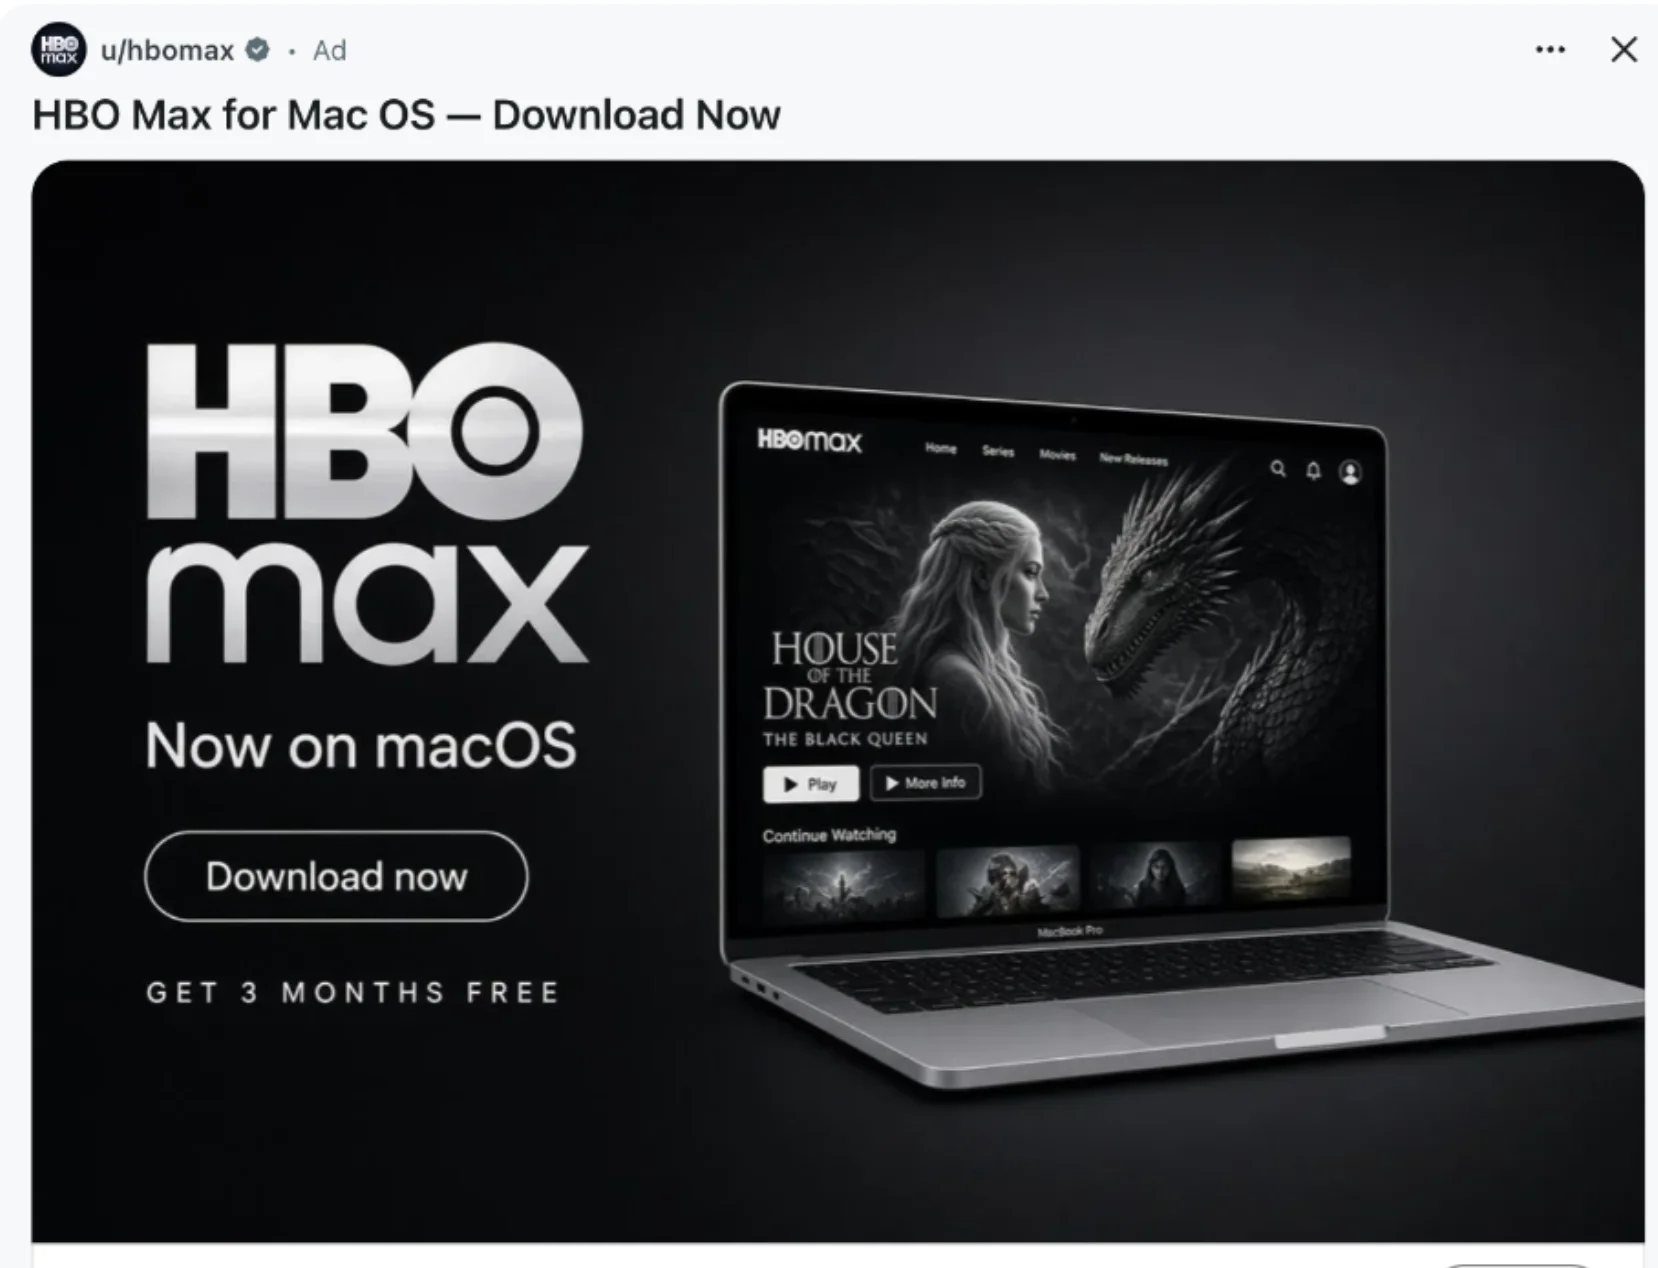
The researchers’ count covers advertisements, not confirmed infections. Their archive grouped the 108 ads into five destinations: two HBO Max lures accounted for 46, while fake Codex, a disk utility and other developer tools accounted for the remainder. This was a compromised advertising identity serving several campaigns, rather than evidence that every HBO Max subscriber was exposed.
According to the joint report, Reddit administrators paused the ads and opened a security investigation. The report does not establish how the account was taken over or how many people ultimately ran a command.
A dead HBO lure led to a live Alfred trap
By the time the investigators examined the infrastructure, the HBO Max domains had stopped delivering their payload. A related page impersonating Alfred, a Mac productivity application, still worked. Crucially, the researchers saw that page offer a malicious installer to a Mac while redirecting a Windows sandbox to the legitimate Alfred website.
That difference explains why one clean-looking visit cannot clear an entire campaign. The server could select what to show based on the visitor’s environment. The Windows redirect was an observation about that particular lure, not proof that PasteSwitch only targeted Macs.
The live Alfred page exposed the next stage. Its copied command fetched a shell script; the script unpacked encrypted content and ran another stage. That stage sent an event=pasted signal to the operation’s tracking infrastructure before retrieving a native Mac executable. The signal recorded the moment the visitor crossed from looking at a web page to running attacker-controlled instructions.
This is ClickFix social engineering: a website turns a supposedly helpful installation or verification task into local code execution. A browser download warning is not a dependable boundary when the visitor starts a system utility and runs the command themselves.
The stolen data outlasted the advertisement
The September Mac payload collected browser credentials and cookies, Keychain material, notes, SSH material and wallet-related data, according to ADAMnetworks’ analysis. It also placed persistence components in hidden directories made to resemble Apple services, including .com.apple.accountsd and .com.apple.metadata.mds beneath the user’s Application Support folder.
Those names are investigation clues, not instructions to delete similarly named legitimate files. Their significance is that closing the fake download page—or removing the first downloaded file—does not necessarily stop code already installed to run again.
The wider PasteSwitch investigation also identified Windows delivery and cryptocurrency clipboard-replacement branches. Those broader findings should not be read as proof that every HBO Max ad delivered every listed malware family. The central finding is a reusable delivery system that chooses among platforms and payloads after the same copied-command handoff. Earlier fake Claude Code ads delivering MacSync illustrate why recognizing a single brand or domain is a limited defense.
The response depends on whether the command ran
If you only viewed an ad or opened the page, that alone does not establish infection through the documented chain. Close it, report the ad, and reach the service through its known website. If you pasted a command but did not execute it, clear it rather than testing what it does.
If you ran it, disconnect the affected device from the network and preserve the URL and approximate time for investigation. Use a separate, trusted device to secure important accounts and revoke existing sessions. Password changes alone may leave stolen sessions usable; device cleanup cannot retrieve data already copied.
On Windows, Defender or another security tool may remove the visible payload while a loader, scheduled task or other persistence remains. A full Gridinsoft Anti-Malware scan is a practical follow-up to the initial containment, alongside account recovery; it is not proof that no information was stolen.
If the page or email made you download an invoice, coupon, tracking app, browser extension, or support tool, scan the PC before opening it again or logging into sensitive accounts.
Scan the affected Windows PCFor an affected Mac, use a security tool compatible with macOS and review unexpected background activity; involve your IT team for a work device. Follow Apple’s account-recovery guidance if your Apple Account was exposed. The durable lesson from this case is specific: a verified advertising account does not authorize a web page to issue commands to your computer.
References
- Kirk, ADAMnetworks, with Hudson Rock. “HBO Max ads exposed the PasteSwitch ClickFix operation.” September 13, 2026. Joint investigation and evidence.
- Microsoft Threat Intelligence and Microsoft Defender Experts. “Think before you Click(Fix): Analyzing the ClickFix social engineering technique.” August 21, 2025. Technical background.
- Apple Support. “If you think your Apple Account has been compromised.” Accessed September 15, 2026. Account-recovery guidance.