BrickLink is back online after a security investigation found access to some members’ usernames and IP addresses, plus a very small number of email addresses. Its November 12 update says passwords and payment information were not accessed. The useful distinction for buyers and sellers is between exposed account identifiers, stolen login secrets and damage to a store’s records: the company’s findings describe different outcomes for each. [1]
The shutdown was an investigation, not evidence of an erased shop
BrickLink says it took the marketplace offline after detecting unusual activity. Before reopening, it worked to contain the issue, investigate what happened and check related access. The notice says affected members have been emailed. It does not identify the intruder, explain the initial entry point or give a total number of affected accounts.
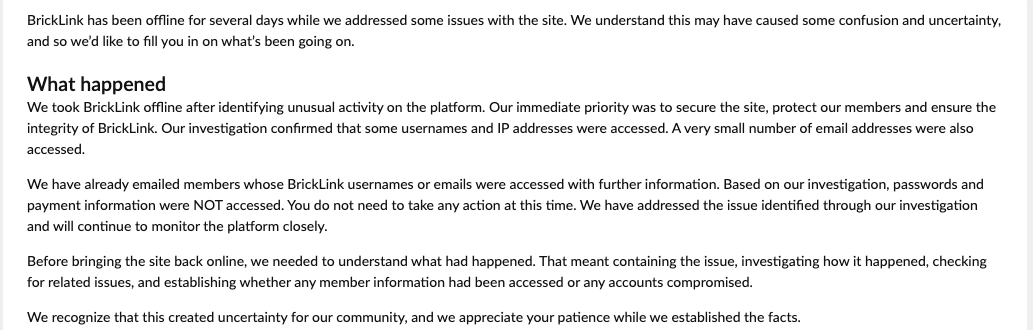
A username or IP address is not a password. That distinction matters when interpreting a breach notice: disclosure of an identifier does not, by itself, establish that someone could sign into the associated account. Equally, a working login does not tell a member whether information about that account was viewed. Those are separate questions, and the notice should be read for the category that actually applies.
Reopened marketplace, one forum still waiting
The current FAQ says the Studio Forum remains offline. It also reports no evidence that orders, wanted lists, messages or store inventories were lost or changed, and waives seller fees for November and December. That is a narrower statement than saying every service has returned or every possible consequence has been ruled out.
If a seller sees an unexpected order or inventory problem, keeping the specific record, time and visible change makes the support request more useful than describing the whole store as “hacked.” BrickLink directs members who notice something wrong to its support team. Sellers should also distinguish a fee waiver from a request to pay a new “recovery charge.” The latter is not a remedy announced in this notice.
Do not apply the 2023 password-reset notice to this incident
Search results still surface BrickLink’s separate November 2023 outage FAQ, which instructed members to reset passwords when the site returned. The November 2026 notice instead says no action is required at this time. Reading the date and incident heading prevents old recovery instructions from being mistaken for a new universal reset. [2]
A subsequent message mentioning the outage still deserves an independent check. Open the marketplace through your own bookmark or typed address before acting on an unexpected request for a password, code or payment. This follows the UK National Cyber Security Centre’s breach-response advice to watch for scam messages and verify requests through official channels. Our guide to recognising phishing messages explains the same separation between a believable story and a trustworthy action path. [3]
For this incident, the immediate task is to read the current notice, check any individual notification and report concrete account discrepancies through BrickLink itself. A restored storefront and a completed investigation of each member’s concerns are different milestones.
References
- BrickLink. Site outage November 2026. Updated November 12, 2026, 15:16 (time zone not specified); accessed November 15, 2026.
- BrickLink. November 2023 site outage FAQ. Historical incident notice; accessed November 15, 2026.
- UK National Cyber Security Centre. Data breaches: guidance for individuals and families. Accessed November 15, 2026.