OpenAI closed a route around ChatGPT Lockdown Mode on September 18, according to research Check Point published on November 5. An HTML preview could open a window outside its sandbox, even with the mode enabled. In the older ChatGPT Classic desktop app, researchers used that window to send messages from a test chat to a server they controlled without a click or approval. [1]
The preview opened a window the sandbox did not contain
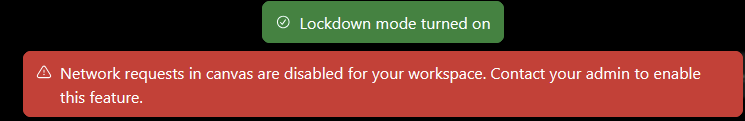
Lockdown Mode limits the ways information can leave a conversation. In Check Point’s test, Canvas refused a request to reach the internet and showed a warning. That was the expected behavior. The researchers found a different path in the preview that renders HTML inside a chat.
ChatGPT displayed the preview inside two nested frames. Its code intercepted the preview’s attempts to open a window and asked the user for approval. But the browser permissions on those frames still allowed pop-ups and let a new window run outside the sandbox. Check Point found that another frame inside the preview could reach the browser’s own window-opening function without going through ChatGPT’s approval check.
That distinction explains how both observations could be true. The preview itself could be cut off from the network while a window opened from it could still send a request. The fix closed the route at the browser permission layer. OpenAI removed the two pop-up permissions from the outer preview frame, and Check Point confirmed in a retest that the technique stopped working. [1]
One opening, two different ways to trick a user
In the desktop demonstration, the researchers had a user converse with a malicious custom GPT. The affected ChatGPT Classic app could open the new window without waiting for a click, allowing the test to send chat messages to an external server. The report describes a controlled demonstration and gives no evidence that real users’ chats were taken through this route.
The same opening could also make a lure look like part of the app. A pop-up in the desktop demonstration kept the ChatGPT app icon while the researchers controlled its title and content. A fake update could therefore arrive in a familiar-looking window. Downloading a file in that desktop scenario still required clicking a link. The report separately showed a shared-chat scenario in a browser that started with a click inside the preview.
What a familiar window tells you
A window can carry an app’s icon while displaying content supplied by someone else. If a chat preview offers an update or asks you to sign in again, close it and start the update or sign-in from the app or site you normally use. A separate ChatGPhish case involving AI summaries shows how the same familiarity can lend credibility to a link.
References
- Alexey Bukhteyev. ChatGPT Lockdown Mode Bypass. Check Point Research, November 5, 2026.