Chainalysis brought Reactor, the KYT web interface and API, and Address Screening back online on November 7. Customers were told to follow new reconnection instructions. Earlier that week, the blockchain analytics company had disclosed that an attacker had obtained names, usernames, password hashes and live tokens for all Chainalysis users.
The November 4 disclosure changed the scope of the breach
In its October 30 notice, Chainalysis said an outside actor had accessed internal systems and tools. The company initially reported exposure of account details such as names and email addresses, but said it had found no evidence that user session tokens or plaintext passwords had been accessed. It also said the incident was separate from the Binance theft.
On November 4, Chainalysis said an on-path attack had exposed passwords for a subset of customers. An on-path attacker can intercept traffic as it passes between two systems; Chainalysis did not publish the technical details of how that happened here. Later the same day, it disclosed the wider exposure of password hashes and live tokens. A password hash is a stored representation of a password. A valid token can authorize requests without the user entering that password again. The two exposures therefore call for different checks during recovery.
Chainalysis said it had no evidence at that point that investigation data had been accessed or that its attribution data had been changed. It did report apparent unauthorized access to some KYT accounts and said it was notifying those customers directly.
Customers could not reset passwords while sign-in was offline
When Chainalysis detected abnormal activity on November 4, it took KYT, its transaction monitoring product, offline along with address screening and the login page. Some users had already received a password reset email. The company told them that they could not yet reset their Chainalysis password, but could change it on other services if they had reused it there.
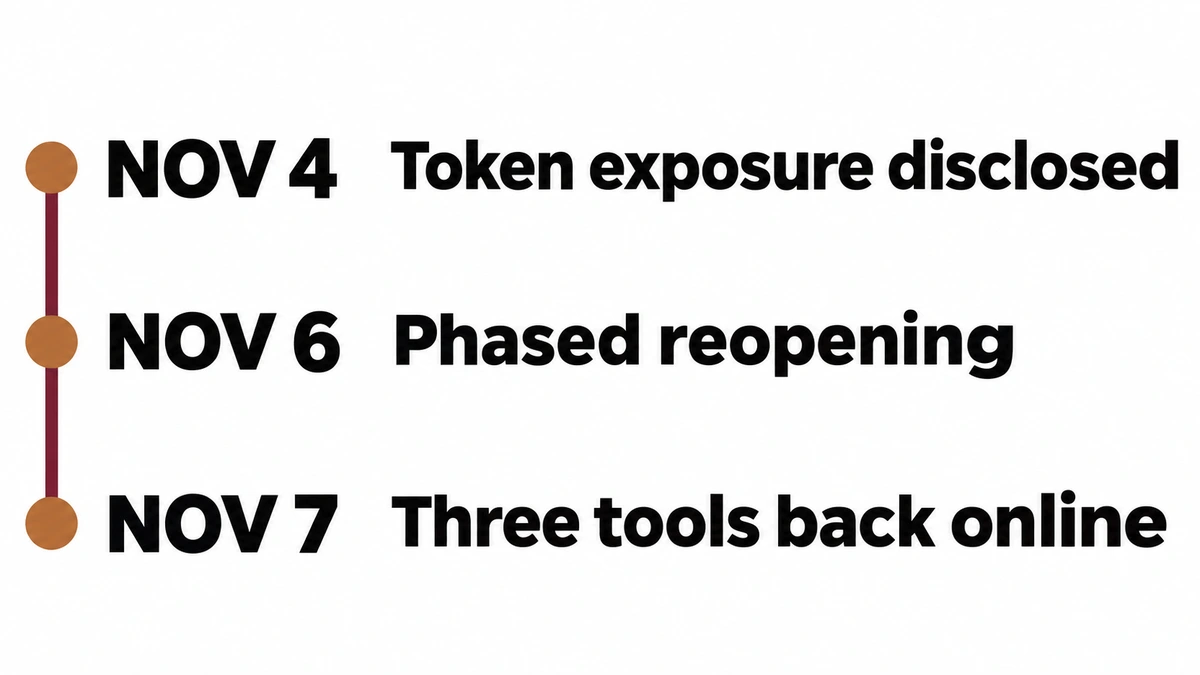
On November 6, the company began reopening KYT and Address Screening in stages. It asked customers to provide trusted IP addresses for its allowlist and prepare to reset passwords and rotate API keys where applicable. Saturday’s notice confirmed the return of Reactor, KYT and Address Screening. It did not say that every other Chainalysis product had been restored.
Reconnect people and integrations separately
Use your usual Chainalysis sign-in page or a known account contact to verify the reconnection instructions before acting on an email. Reset the user password there when access is available. If your organization connects to KYT through the API, follow Chainalysis’s key rotation instructions and confirm that the integration is receiving transaction screening results again. A working browser login does not establish that an automated integration has resumed.
The Railway API key incident illustrates a related distinction: operators may have to restore an application’s credentials separately from their own access.
References
- Chainalysis Team. Chainalysis Security Incident Information. Chainalysis, October 30, 2026; updated November 7, 2026. Accessed November 9, 2026.