Un_A.exe: Temp Uninstaller or Malware Lookalike?
Learn why NSIS creates Un_A.exe, how to identify its parent app, and when a Temp copy, stale entry, or recurring process needs cleanup.

Keyv npm Worm Poisoned 444 Packages: Check Before Rotating Tokens
The Keyv npm worm poisoned hundreds of packages and can react when a stolen GitHub token is revoked. Check persistence first, then rotate credentials safely.
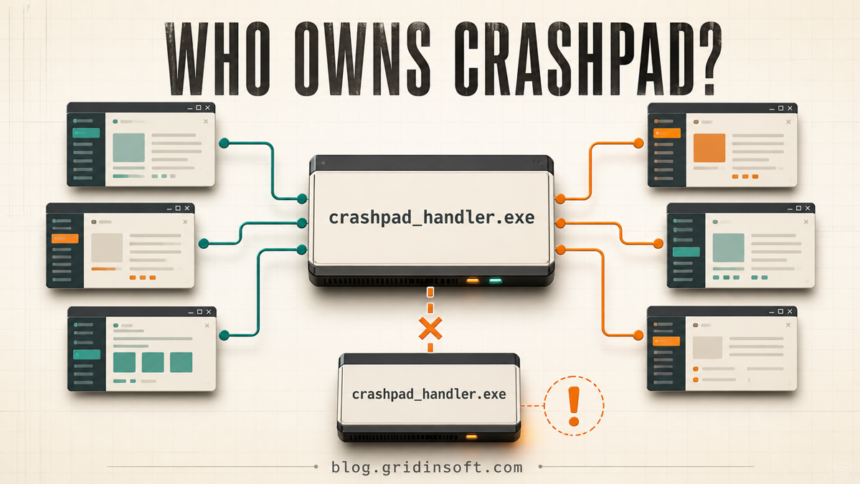
crashpad_handler.exe: Safe Process, Parent App, and Error Fix
Learn what crashpad_handler.exe does, identify its parent app, fix Application Error or high CPU, and check a suspicious copy safely.
Heisenberg RAT: Claims, Hidden Desktop Risk, and Removal
See what is verified about Heisenberg RAT, how hidden desktops can expose browser sessions, and how to isolate, scan, and recover accounts safely.
Malware Modified Your Git Commits? PolinRider Recovery
Find PolinRider Git rewrite artifacts, preserve commit evidence, clean affected repositories and developer systems, and rotate exposed credentials.
iPhone .mobileconfig Phishing: Opened vs Installed
Learn what opening, downloading, or installing a .mobileconfig profile changes on iPhone and how to remove an unknown profile safely.

Pass-ta-key Attack Lets Malware Hijack Google Passkeys
Unit 42 showed how malware on Chrome for Windows can abuse synced Google passkeys. Learn who is affected, what was fixed, and how to recover safely.
N-central CVE-2026-18577: Patch and Hunt for Cloudflared
N-central needs HF4 build 2026.3.1.14. Check appliance accounts and API logs, then investigate Take Control sessions and downstream persistence.
Quick Driver Updater Removal: Stop qdu.exe and Leftovers
Remove Quick Driver Updater, qdu.exe, recurring scheduled tasks, and leftovers, then safely recover from unwanted driver changes.
Trojan:Win32/Suweezy Keeps Coming Back: Removal Guide
Remove Trojan:Win32/Suweezy, check Defender exclusions and persistence, verify a CrystalDiskMark download, and stop the alert returning.
Arch Freezes AUR Pushes After Malware Wave: Check Your System
Arch temporarily stopped AUR pushes after malicious package takeovers. Check openconnect-sso exposure, Linux persistence, stolen secrets, and the right recovery order.
Rails CVE-2026-66066: Patch Active Storage and Rotate Secrets
Rails patched CVE-2026-66066 in Active Storage. Check whether your app uses vulnerable libvips processing, update, rotate exposed secrets, and inspect official forensic evidence.