USB Shortcut Virus: Remove Shortcuts and Restore Hidden Files
Remove a USB shortcut virus safely: do not open .lnk shortcuts, scan the PC and USB, restore hidden files with attrib, delete leftovers, and format after backup.

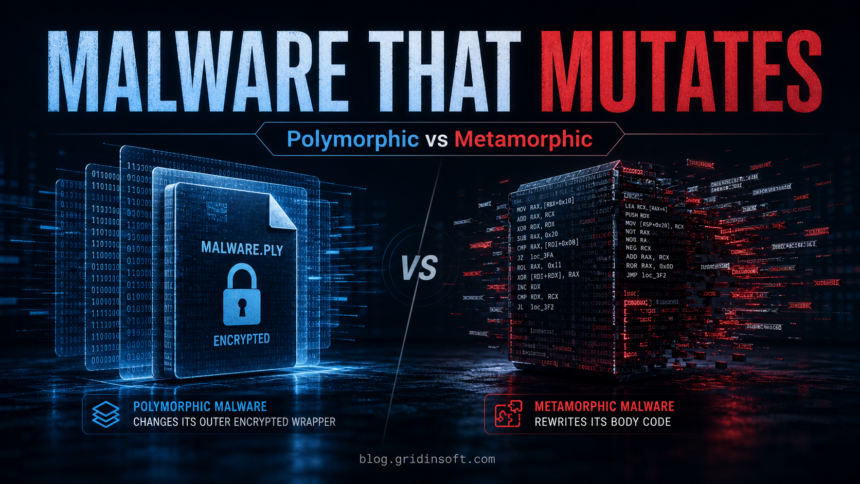
Polymorphic vs Metamorphic Virus: Key Differences
Polymorphic malware changes its encrypted wrapper; metamorphic malware rewrites its code. Learn the difference, detection signs, examples, and safe removal steps.

Fake Instagram Hacking Services
Instagram hacking scams is an old-new direction of online fraud that targets people who want to get into someone’s accounts on social media. Frauds poison search results, gather the users…
Whaling Phishing: CEO Fraud
Whaling phishing targets executives and privileged users with fake payment, payroll, access, or data requests. Learn warning signs, examples, and what to verify before you approve.

Stopabit Virus
Stopabit is an unwanted application that has almost no useful functionality. Users can see its promotions as a useful tool for screen time control, but it in fact aims at…
Weather Zero Virus or Adware? High CPU and Removal Guide
Weather Zero can run WeatherZeroService.exe, use high CPU, show ads, and leave stubborn files. Learn how to uninstall it, stop the service, and clean leftovers.

Bloom.exe
Bloom.exe is a malicious miner that masquerades as a legitimate process. Its job is to use the victim's device to mine cryptocurrency for con actors. The most visible sign of…
Email Security Tips: Inbox Safety
Email security tips for spotting phishing, blocking fake invoices, checking hidden forwarding rules, scanning risky attachments, and recovering a hacked inbox safely.

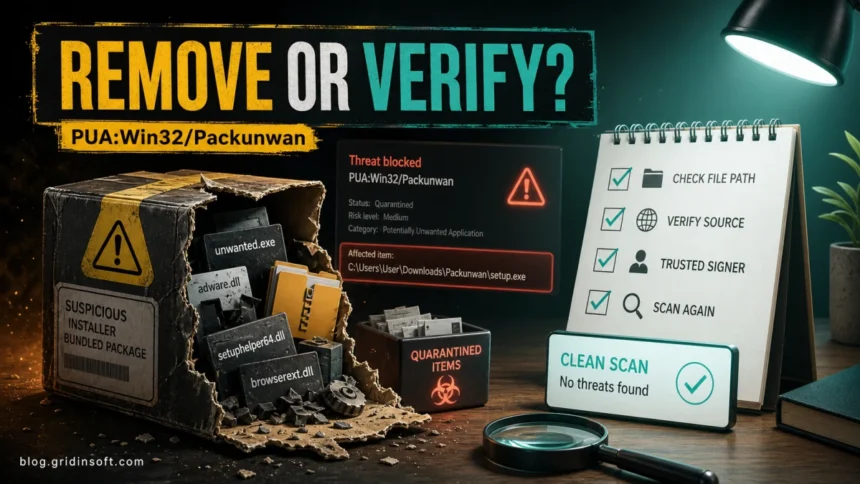
PUA:Win32/Packunwan: Remove, Adsunwan, or False Positive?
Defender found PUA:Win32/Packunwan or Adsunwan? Check the path, remove risky source packages, and verify trusted game or mod files before restoring anything.
Trojan:Win32/Casdet!rfn: Meaning, False Positive, and Removal
Defender found Trojan:Win32/Casdet!rfn? Learn what the alert means, when a false positive is possible, and how to remove risky files safely.
Trojan:Win32/Tnega!MSR: False Positive or Remove It?
Seeing Trojan:Win32/Tnega!MSR? Check the affected path, source, signature, false-positive clues, and safe removal steps if the alert keeps returning.


InstallCore Malware? PUADlManager:Win32/InstallCore Guide
InstallCore is a bundler/PUA detection, not always a classic virus. Check Microsoft and F-Secure context, remove bundled apps, browser changes, and leftovers.